UnrealIRCd CVE-2026-114713 Exploited: An Unescaped IRCv3 Label Tag Lets Any User Inject Server Commands — Hot-Patch Now, CISA Adds It to KEV
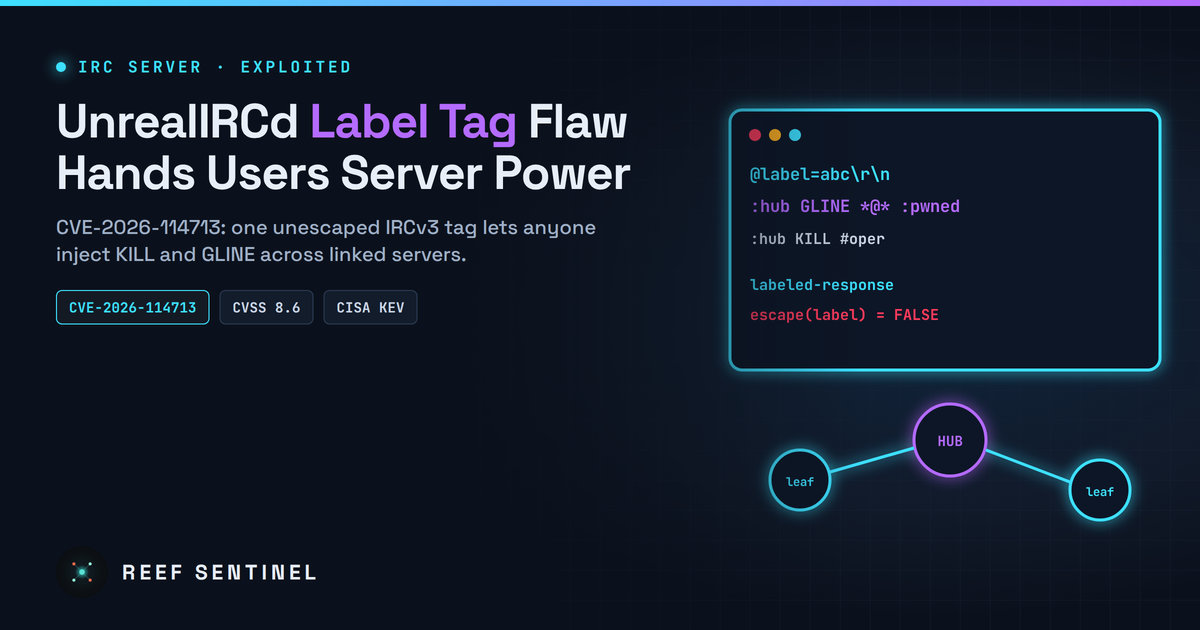
An escaping bug in UnrealIRCd 6's labeled-response module lets any user on a linked network issue commands such as KILL and GLINE with server authority, and attackers began exploiting it within two days of the fix.
UnrealIRCd's maintainers call CVE-2026-114713 the most critical flaw in the IRC server's 15-year history, and it is now being exploited. Any ordinary user on a network of linked UnrealIRCd 6 servers can smuggle server-to-server commands through an IRCv3 message tag. The servers then carry them out with full server authority. CISA added the flaw to its Known Exploited Vulnerabilities (KEV) catalogue on 13 November.
What Happened
The project announced a critical security release on 4 November. It shipped UnrealIRCd 6.2.7.1 and a hot-patch on Saturday 7 November at 19:00 Mauritius time (15:00 UTC). The release fixes nine security issues, including the critical CVE-2026-114713.
The maintainer says the bugs were found in an internal, AI-assisted code audit. The first advisory made no claim of exploitation. On 9 November the project added a warning: "We are seeing bad guys exploiting this issue on the internet right now." CISA's KEV listing followed four days later.
Technical Details
IRCv3 lets clients attach a label tag to a command, and the server echoes that label back in its reply so the client can match responses to requests. The labeled-response module in UnrealIRCd 6.0.0 up to 6.2.7.0 copied the label into its replies without escaping it.
IRC is a line-based text protocol, so a label containing newlines and other control characters can end the current line and start a new one. When that reply travels between linked servers, the injected line is treated as a genuine server-to-server command. According to the maintainers, an ordinary user can therefore issue commands such as KILL and GLINE with server authority. That means disconnecting users or banning them network-wide, and more.
The CVE record scores the bug CVSS 8.6 (AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:H/A:N) and classifies it as CWE-140, improper neutralisation of delimiters. Exploitation needs a network with two or more linked servers, which covers most real IRC networks.
The same release fixes eight lesser issues:
- two different ways for a user to reveal another user's IP address
- a blacklist recheck that can hang the server
- a crash on
CHGIDENTfrom Services that a normal user can trigger - a counting error that makes every new connection get "This server is full"
- a ban-limit bug for Services
- a possible flood through TLS renegotiation
- a possible crash in whowasdb
Who Is Affected
- UnrealIRCd 6.0.0 through 6.2.7.0: vulnerable. Fixed in 6.2.7.1 or by the hot-patch.
- UnrealIRCd 5: affected. It has been end-of-life since July 2023 and gets no fix, only a workaround.
- Older 3.2.x and 4.x: not checked by the project. The maintainer warns that several of the other bugs probably go back that far.
Distribution packages, such as Alpine's, have released their own fixed builds.
Patch Status
On Linux and other Unix systems, the hot-patch applies without a restart:
./unrealircd hot-patch bundle-20261107Confirm it worked (UnrealIRCd 6.0.2 and later):
./unrealircd module-status | grep labeled-responseThe module should report either hot-patch-bundle-20261107 or 6.2.7.1. Windows servers need the full upgrade to 6.2.7.1 and a restart. On UnrealIRCd 5, add the following to the configuration of every server, then do a full restart (a rehash is not enough):
blacklist-module "labeled-response";What To Do Now
- Patch every server on the network, not only the hubs. Injected lines cross links, so one unpatched leaf is enough.
- Until every server is patched, apply the project's IRCOp spamfilter workaround, which blocks labels containing illegal characters. It protects linked servers only if all of them run 6.0.4 or newer. Copy the exact regex from the official advisory.
- Check logs since 7 November for unexpected
KILL,GLINE,ZLINEorSPAMFILTERactions that no operator issued. Check for bans or server-level changes that nobody on the oper team recognises. - Look for joins with unusually long or malformed
label=tags in client traffic. - Move any remaining UnrealIRCd 5 or older servers to 6.2.7.1.
Why It Matters
IRC still runs community chat for open-source projects, gaming and private groups, and it still serves as command-and-control for older botnets. Network-wide server authority lets an attacker silence or ban whole communities, or quietly take over channels. The case also shows something broader: an AI-assisted audit turned up a decade's worth of bugs in a mature codebase, and attackers were exploiting the critical one within about two days of the fix.
