Meta and Signal Tell Canada's Senate They Could Leave Rather Than Weaken Encryption: Big Tech's Last Push to Rewrite Lawful Access Bill C-22
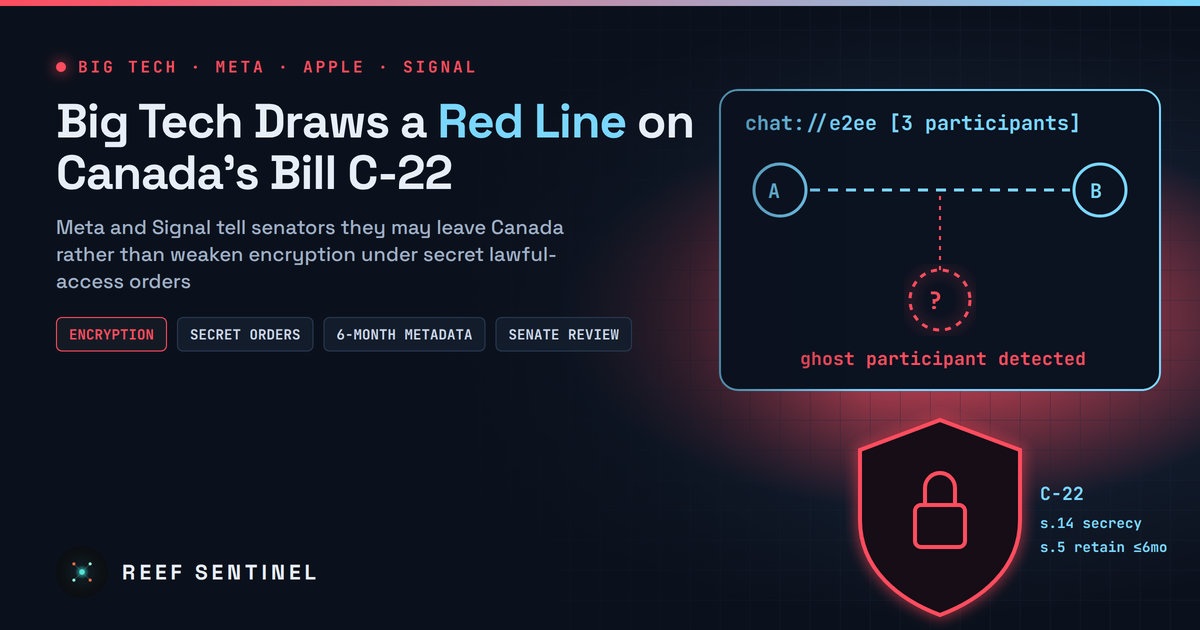
At a Senate hearing on Canada's Bill C-22, Meta said it would refuse orders that weaken encryption and could pull services, Signal said it would leave rather than compromise users, and Apple says the amended bill still threatens its security features.
What Happened
Canada's lawful-access bill is getting its last serious review before it can become law, and the biggest platform companies are using that review to make clear they will not back down. On Monday 16 November 2026, the Senate's national security committee heard from Meta, Signal and the networking company Tailscale as it studies Bill C-22, the Lawful Access Act, 2026. Apple and Google have also kept up pressure on Ottawa to rewrite the bill.
Two warnings stood out:
- Meta: Rachel Curran, head of public policy at Meta Canada, said the company would refuse any order that weakened its encryption. She pointed to Apple's decision to pull an encrypted iCloud feature from the UK and said Meta would have to consider the same option in Canada.
- Signal: Udbhav Tiwari, vice-president of strategy and global affairs, told senators that if Signal had to choose between betraying its users and leaving Canada, it would not compromise Canadians' security.
Tailscale's chief executive, Avery Pennarun, called for "fine tuning" to avoid "unintended side effects". He said the company is considering moving some services abroad, or licensing its technology overseas without its Canadian branding.
What the Bill Actually Does
Bill C-22 was introduced on 12 March 2026. It passed all its House of Commons stages on 18 June, with government amendments, and was referred to the Senate committee on 22 October, according to Parliament's official record. It has three parts:
- Part 1 amends the Criminal Code, the CSIS Act and other laws to expand police and intelligence access to data and subscriber information.
- Part 2 creates a new Supporting Authorized Access to Information Act. This sets obligations for "electronic service providers", a term broad enough to cover messaging apps, cloud platforms and VPNs as well as telecom carriers.
- Part 3 provides for a parliamentary review of the first two parts.
The disputed powers are mostly in Part 2:
- Metadata retention. Regulations can require "core providers" to keep categories of metadata "for reasonable periods of time not exceeding six months". Message content, web browsing history and social media activity are excluded. Who contacted whom and location records are not.
- Capability orders. The Public Safety Minister can order a provider to build or keep surveillance capabilities.
- Secrecy. Section 14 bans a provider from revealing what an order says and even "the fact that the electronic service provider is or was subject to the order". Disclosure is allowed only in limited cases.
- An encryption carve-out with a catch. Providers do not have to comply if doing so would introduce a "systemic vulnerability" or stop them fixing one. Separately, the bill says providers do not have to decrypt data, except where the provider supplied the encryption itself and holds what is needed to decrypt it.
The government says critics have this wrong. A spokesperson for Public Safety Minister Gary Anandasangaree has said the bill "does not authorize indiscriminate surveillance" and does not permit or compel companies to introduce systemic vulnerabilities or backdoors.
Why the Companies Are Not Convinced
The fight is over the drafting of those safeguards. Critics make three main points.
- The "systemic vulnerability" test is narrow. The bill defines it as a weakness in a service's electronic protections that "creates a credible risk". Companies say that leaves the government a lot of room to decide what counts. Meta has called the definition unclear.
- "Ghost participants" may not count as breaking encryption. Signal and other witnesses warned that an order could require a service to quietly add a hidden participant to an encrypted conversation. The encryption itself would stay intact, but the conversation would no longer be private. Tiwari asked for independent technical assessments before any order takes effect. He argued that AI tools able to find and exploit weaknesses make any deliberately added access point more dangerous.
- Secrecy blocks transparency. Apple raised this in May, when it said it would "never" build backdoors and warned it might have to withdraw some products from Canada. Because orders are secret, a company may be unable to tell its users that its security has changed. Apple has since said the House amendments still do not go far enough.
Security commentators who testified also asked for the "indiscriminate" metadata-retention requirement to be dropped altogether.
Why It Matters
This goes well beyond Canadian politics. A law like this shapes how global platforms are built.
- The UK precedent is now a real option. In 2025 Apple removed Advanced Data Protection for iCloud for new UK users rather than comply with a secret UK order. Meta has now said publicly, in a legislature, that it would consider the same response in Canada. Withdrawing a feature this way leaves users in that country with weaker default protection.
- Secret orders weaken trust in any vendor. If a provider cannot say whether it is under an order, security teams cannot fully verify the security claims of any service operating in Canada.
- Metadata is sensitive data. Six months of contact and location records for a whole user base is an attractive target. It would need breach-grade protection from every provider required to keep it.
What It Means for Users and IT Teams
- Organisations with Canadian operations should list which of their providers (messaging, VPN, collaboration, cloud) could be classed as "core providers", and track whether they say they will stay, change their service or leave.
- Encryption design will matter more. Under the bill's own wording, data encrypted with keys only the customer holds is better protected than data encrypted with keys the provider holds. Customer-managed keys and true end-to-end encryption are worth reviewing for sensitive work.
- Plan for features disappearing. Teams that rely on Signal, WhatsApp or encrypted VPN services in Canada should prepare a fallback in case a provider limits its service there.
- Users elsewhere should watch closely. Canada sits in the Five Eyes alliance with the UK, and lawful-access designs often spread between allied countries.
What Happens Next
The bill is still at committee stage in the Senate. The committee can propose amendments before report stage and third reading. If the Senate changes the text, it goes back to the House of Commons. The companies want three changes: stronger protection for encryption, independent technical review of orders, and no blanket metadata retention. Whether senators adopt any of these will decide whether Canada becomes the next market where major platforms switch off security features.
