Dragos Seeded 2 Million Bait AI Prompts: Three Providers Breached Unaware, Resellers Logged Prompts, 'Zero Data Retention' Leaked — OpenRouter Pulls ZDR Label From MiniMax Endpoints
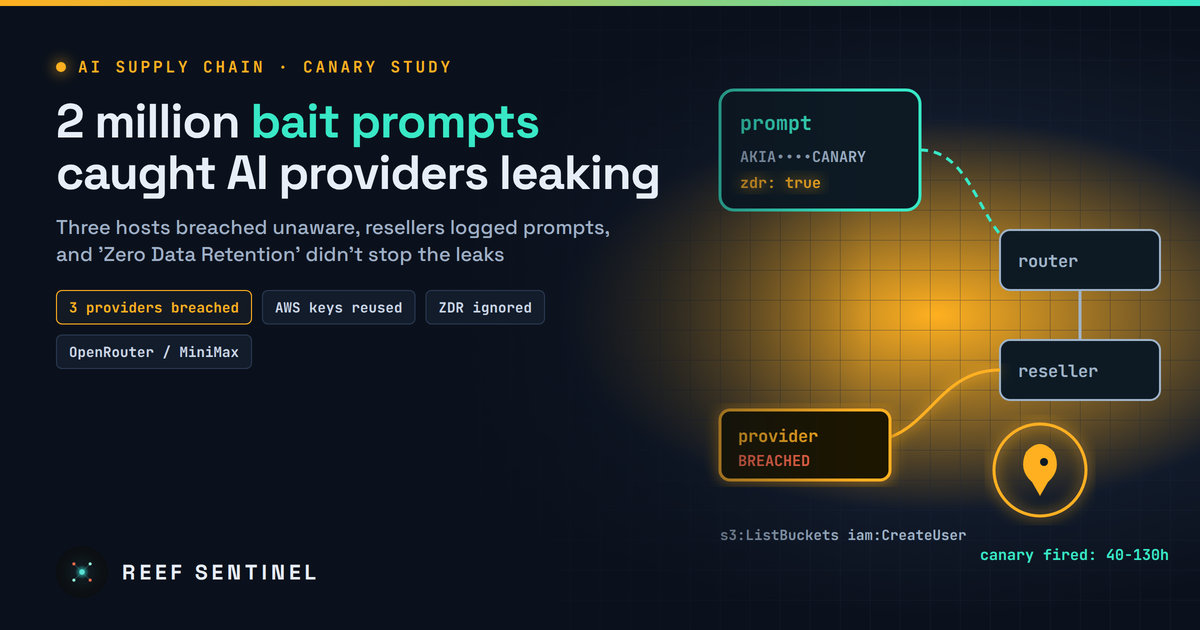
A five-month canary experiment found three AI hosting providers breached without their knowledge, marketplace resellers keeping customer prompts, and ZDR-flagged requests read by third parties, prompting OpenRouter to strip the ZDR label from MiniMax-model endpoints.
What Happened
Dragos chief research officer HD Moore has published the results of a five-month experiment that sent about two million bait prompts to widely used AI services. The findings: at least three AI hosting providers were breached without knowing it, some marketplace resellers kept customer prompts, and requests marked "Zero Data Retention" (ZDR) still ended up in other people's hands.
Between July and November 2026, the team put unique canary secrets into the prompts. These were AWS access keys tied to empty, fully logged accounts, plus one-off URLs, DNS names, and git, SSH, database and mail credentials that existed nowhere else. Dragos ran the infrastructure behind each canary and logged every connection. If a secret was used, the prompt carrying it had been read by someone other than the model.
The report came out on 19 November. Two days later OpenRouter customers began publicly posting an email from the AI routing platform, titled "Requests you sent to MiniMax models may have been read". It appears to describe the same kind of canary testing. OpenRouter has not published a public page about it.
Three Providers Breached, Keys Used Within Hours
Dragos says data from "at least three AI providers" was exposed. The earliest incident dates to mid-July, and none of the three providers knew until Dragos told them. Dragos has not named them. It says one has not disclosed its breach publicly and another posted a preliminary notice in late October.
The largest breach covered "a couple hundred" bait AWS keys, each sent in a single request during late October. The researchers say those keys were then used for tens of thousands of AWS API calls. In one example, a key planted on 21 October was first used the next day and was still being used three weeks later. Some stolen keys came from requests the provider had rejected before any model ran. That means the attackers were reading raw request traffic, not model output.
Once inside the empty accounts, the attackers followed a familiar cloud playbook:
- They tested the keys and listed S3 buckets
- They searched Secrets Manager and Parameter Store for more credentials
- They tried to turn on Amazon Bedrock models and create Bedrock API keys
- They added IAM users to keep access
Their tooling also changed over time. They started with a script running from Chrome on Windows, moved to Boto3 inside OrbStack, then to the AWS CLI on Kali Linux. From 1 November they brought in ARTEX, an LLM-driven pentest framework, which showed up with the user agents artex-agent and artex-judge-r121. ARTEX is the same tool CERT-EU linked to this month's attack on European Commission staff systems.
Resellers Read Prompts Without Hacking Anything
The second finding needed no breach at all. Dragos says several resellers on an AI inference marketplace "were able to view and retain customer prompts using standard logging". To isolate them, the team sent identical prompts through different sellers. The secrets came back only from certain sellers, so the leak followed the seller, not the marketplace. In one case, secret URLs were opened about a day and a half after the prompt. The report also describes root SSH login attempts using a password that existed only inside a prompt.
"Zero Data Retention" Only Binds the First Hop
The most uncomfortable finding for enterprise buyers is about privacy flags. Dragos says prompts sent to US-based providers were passed on to Chinese AI organisations. One Chinese AI lab fetched secret URLs from more than half the prompts sent to its models between July and October, including about two-thirds of requests marked "no data collection" or ZDR.
In one case, Dragos says, a secret link from a ZDR request turned up 24 days later in a Feishu workplace chat. Within two minutes it was opened from three desktops and three phones in Beijing and Shanghai. The report's point is simple: a privacy flag only binds the first hop. If a provider forwards your request to the model's original developer, your setting may not go with it.
OpenRouter's email fills in names that Dragos left out. According to copies customers posted, a researcher placed unique URLs in prompts sent to MiniMax models from July to October 2026. A third party opened them "40 to 130 hours after the requests were sent", whether MiniMax served the request itself or another provider forwarded it. OpenRouter says AtlasCloud, Novita and StreamLake told it they forwarded OpenRouter requests for MiniMax models to MiniMax. It says the issue "sits with MiniMax and the providers that forwarded to it, not with OpenRouter".
MiniMax reportedly told StreamLake that content moderation was switched on for its endpoints before 22 October and that it has since enabled ZDR. OpenRouter says it has asked MiniMax for its own account and has not received one. In the meantime it has removed the ZDR label from these MiniMax-model endpoints. The email also says tests on other models at the same providers were not accessed, with one exception, and that none of the AWS test keys from those requests were used.
OpenRouter's own data processing agreement already warns about this. It says inclusion on its ZDR list reflects a provider's represented policy and is not a guarantee that the provider complies.
Who Is Affected
Any organisation whose staff or applications send sensitive data to AI models through aggregators, routers or reseller marketplaces should assume some of those prompts may have been stored or read. This matters most for coding agents that paste environment files, logs or config into prompts, since these often contain live keys. Dragos says it is working with about a dozen providers. It warns that stolen keys and secret URLs "continue to be accessed, even months after the initial incident."
What To Do Now
Dragos's guidance, plus standard incident steps:
- Rotate anything that went into a prompt. If cloud keys, tokens, passwords or internal URLs were ever pasted into an AI tool, especially through a router or cheap reseller, treat them as exposed and rotate them.
- Shorten the supply chain. Self-host where you can afford it. Otherwise use a first-tier provider under one contract and one privacy policy, and avoid reseller marketplaces for sensitive work.
- Pin your upstream. On routing platforms, pick providers explicitly, use allowlists, and check where requests are actually served. Do not rely on a ZDR badge alone.
- Seed your own canaries. Put unique canary credentials and URLs in internal AI pipelines and treat any use as an incident.
- Filter secrets before they leave. Turn on provider-side secret filtering and add client-side redaction, knowing neither catches everything.
- Hunt in CloudTrail. Look for the ARTEX user agents, unexpected Bedrock enablement or API key creation, and new IAM users.
For example, to search CloudTrail for the ARTEX user agents:
aws cloudtrail lookup-events --max-results 50 \
  --query "Events[?contains(CloudTrailEvent, 'artex-')].[EventTime,EventName,Username]" \
  --output table
Why It Matters
Companies have spent two years writing AI acceptable-use policies around one question: does the vendor train on our data? This research shows that is the wrong question. A prompt can pass through a router, a reseller, a hosting provider and the model's original developer, each with its own logging, moderation and security posture. Any of them can be breached. Without canaries, none of this was visible to the customers, and much of it was not visible to the providers either.
