Frappe Email Flaw GHSA-vwqr-4mjv-ffrm Exploited: Any Logged-In Website User Could Send Phishing Through Your ERPNext Mail Server and Attach Private Files — Update to 15.127.1 or 16.60.1
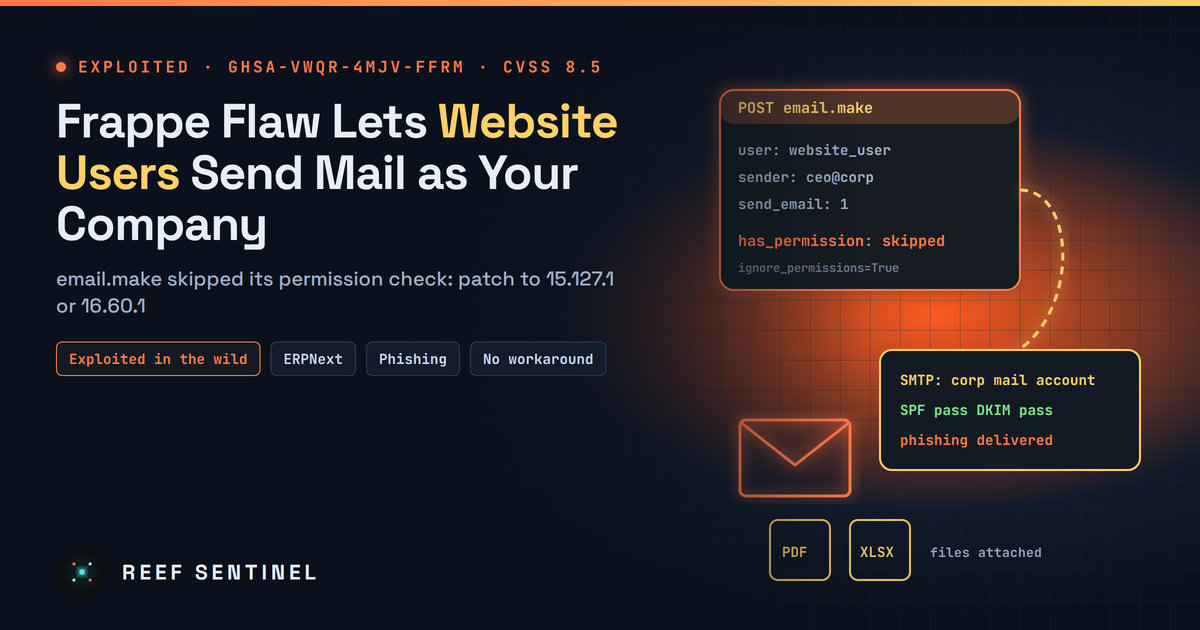
Frappe's maintainers confirm in-the-wild exploitation of a CVSS 8.5 authorization flaw in email.make that let any authenticated user, including self-registered portal users, send spoofed email through the organisation's mail account and attach files they should not see; there is no workaround, so upgrade to 15.127.1 or 16.60.1.
What Happened
The maintainers of Frappe Framework, the open-source Python platform behind ERPNext, Frappe HR, Helpdesk, LMS and many custom business portals, have published a high-severity advisory, GHSA-vwqr-4mjv-ffrm. It covers a broken authorization check in the email communication feature. The advisory states plainly: "This flaw has been exploited in the wild."
The bug lets any logged-in user, including a low-privilege Website User, send email through the organisation's own configured mail account and make it look as if it came from another sender. The advisory says it can be used "for spam or phishing in the organisation's name" and that it "could expose some files the user is not permitted to access."
The fixed releases, Frappe 15.127.1 and 16.60.1, went out on 18 November at 01:32 and 01:54 Mauritius time (17 November, 21:32 and 21:54 UTC). The advisory followed on 19 November. GitHub rates it CVSS 8.5 (AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:H/A:N) and classes it as CWE-863, Incorrect Authorization. No CVE ID had been assigned when we checked. The maintainers say there is no workaround and upgrading is the only fix.
Technical Details
The vulnerable code is frappe.core.doctype.communication.email.make, a whitelisted server method. That means any authenticated session can call it over Frappe's standard /api/method/ interface. It is the method behind the "New Email" dialog that staff use to send a quotation, invoice or reply straight from a document.
The pre-patch code in 15.127.0 shows why it was so easy to abuse:
- The only authorization step was a document-level check,
frappe.has_permission(doctype, doc=name, ptype="email"). It ran only if the caller named a reference document. A request with no reference document skipped the check completely. - The method then passed the caller's inputs to an internal helper that its own docstring describes as one that "ignores Permission checks". That helper inserts the Communication record with
ignore_permissions=True. - The caller controls the sender address, the sender's display name, recipients, CC/BCC, subject, HTML body and a scheduled send time. When the "send email" option is set, the message goes out through the site's default outgoing email account.
- The method also accepts attachments as names of existing File records and attaches them to the new message. That fits the advisory's warning that some files the user should not see could be exposed.
The advisory's own wording is that "an existing authorization check could be satisfied by users who were not meant to send email from the site." In other words, the check that existed was too weak for the job.
The fix, merged as pull request #47833 (15.x) and #47834 (16.x), adds one line of policy before anything else runs. If the caller is not a System User (Frappe's term for staff accounts with desk access), the request fails with "Not permitted". The pull request says simply: "Website Users have no need for this."
We are not publishing request details. The advisory's proof-of-concept is one sentence: a minimally privileged authenticated user sends a crafted request to the affected endpoint.
Who Is Affected
- Frappe Framework below 15.127.1 (version 15 line) and 16.0.0 up to but not including 16.60.1.
- Every app that runs on an affected framework version inherits the flaw, including ERPNext, Frappe HR, Helpdesk, CRM, LMS and in-house apps. The framework version is what matters, not the app version.
- Risk is highest on sites that let the public register (customer and supplier portals, e-learning sites, helpdesks, job portals). There, an attacker can create their own Website User account and needs no stolen credentials. On sites without self-signup, any existing portal user or compromised low-privilege account is enough.
- Organisations whose outgoing mail account has good sender reputation and proper SPF, DKIM and DMARC are, ironically, the most valuable targets. Mail sent through their real server passes authentication checks that a spoofed message from outside would fail.
Patch Status
The patches are out. Update to Frappe 15.127.1 or 16.60.1 (or later). Self-hosted bench installations can update with the usual workflow:
bench --site all backup
bench update
bench version   # confirm frappe 15.127.1+ or 16.60.1+
Frappe Cloud customers should check that their bench group is on a release that includes the fix. Where automatic updates are not enabled, deploy one. Forks and vendors that pin Frappe to an older tag need to pick up the backported commit themselves.
What To Do Now
- Upgrade first. There is no configuration switch that closes this hole.
- Review outgoing mail. In the desk, open the Communication and Email Queue lists. Look for messages created by Website Users or other non-staff accounts, unfamiliar sender addresses or display names, bulk recipient lists, and mail sent at unusual hours.
- Check your mail provider's side too. SMTP relay logs, sending quotas, bounce spikes and spam complaints can show abuse that has already left your server. Watch for blocklisting of your sending domain or IP.
- Look at attachments. Communications carrying File records unrelated to the sender, such as invoices, payroll exports or private uploads, may mean data was exfiltrated by email.
- Audit portal accounts. Remove or disable suspicious recent self-registrations. If you don't need public signup, turn it off in Website Settings.
- Warn customers and partners if you find phishing sent in your name, so they don't trust messages that pass your SPF and DKIM.
- Rate-limit and alert on outbound mail volume from the application server, so the next abuse of a legitimate sending path shows up quickly.
Why It Matters
This isn't a remote-code-execution bug, and that is why it is easy to underrate. Attackers don't need a shell when they can borrow a company's trusted mail server. Phishing sent from an organisation's real infrastructure, with valid authentication and a familiar sender, is far more convincing than anything sent from a lookalike domain. That matters most for ERP systems that routinely email invoices, purchase orders and payment details to customers and suppliers.
The flaw also shows a common pattern in web frameworks. A permission check sits behind a condition ("only if a document was named"), and an internal helper deliberately bypasses permissions on the assumption that the caller has already been vetted. When the outer check can be skipped, the inner trust becomes the vulnerability. Teams that build on Frappe should review their own whitelisted methods for the same shape. Any endpoint that only checks permissions when an optional argument is present deserves a second look.
