VMware vCenter CVE-2026-123890 Was a Zero-Day for Two Months: China-Linked ARMORY CASTLE Forged Golden SAML, Took Over ESXi and Pulled AD Secrets From VM Disks
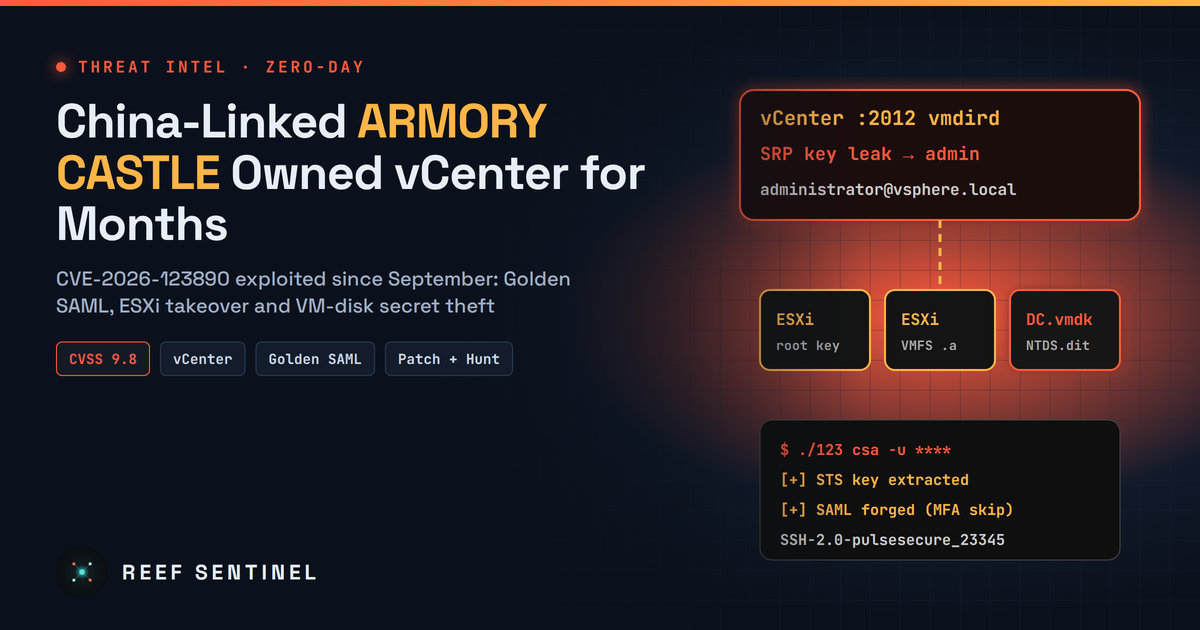
Google and Mandiant say suspected China-nexus group ARMORY CASTLE exploited the vCenter vmdird authentication bypass CVE-2026-123890 since early September, chaining a BeyondTrust zero-day, six custom tools and Golden SAML to steal domain secrets straight from virtual machine disks.
Overview
Google Threat Intelligence Group (GTIG) and Mandiant say the critical VMware vCenter authentication bypass that Broadcom patched on 19 November, CVE-2026-123890 (CVSS 9.8), was used as a zero-day for at least two months. They attribute the attacks to ARMORY CASTLE, a suspected China-nexus espionage group formerly tracked as UNC5221. The report, published on 20 November 2026, is the first public evidence that the bug was exploited before the fix. Our earlier coverage of VMSA-2026-0009 dealt only with the patch. What's new is the full intrusion chain, six malware families and utilities, network indicators and detection rules.
The investigators say a "small number" of organisations are confirmed compromised and more are probably affected. The group did not attack vCenter from the internet. It got in through an earlier BeyondTrust Remote Support zero-day (CVE-2026-102764), moved to an internal Linux appliance with no endpoint monitoring, and attacked vCenter from inside. From there it forged administrator sessions, took over ESXi hosts and pulled domain-controller secrets straight out of virtual machine disks.
The Vulnerability
CVE-2026-123890 is in the VMware Directory Service (vmdird) on the vCenter Server appliance. GTIG describes it as an unauthenticated SRP-6a session key disclosure over DCE/RPC on TCP port 2012, caused by predictable UUIDv1 timestamp generation in the SRP interface. Anyone who can reach that port can get an authenticated session as administrator@vsphere.local without a password.
Broadcom's VMSA-2026-0009 (19 November) bundles the fix with four other issues, in SDDC Manager and in VMware Tools for Windows, and lists no workaround. Fixed builds reported for the vCenter bug include vCenter 8.0 U3m, VCF/vSphere Foundation 9.0.2.0200 and 9.1.1.0200, and VCF 5.2.5. Check the advisory for your exact build. Organisations still on vCenter 7.0 should contact Broadcom about extended support.
When this was written, CVE-2026-123890 was not yet in CISA's Known Exploited Vulnerabilities catalog. Given GTIG's findings, we expect it to be added.
Timeline
- Early 2025: the LAZYBONES backdoor is seen in an earlier ARMORY CASTLE campaign that exploited Ivanti CVE-2025-22457.
- 13 July 2026: build timestamp inside the BONESAW exploit binary (Go metadata can be faked).
- 29 July 2026: a related vmdir LDAP authentication bypass, CVE-2026-59309, is disclosed.
- Early September 2026: BONESAW is run against a vCenter that was already patched for CVE-2026-59309. This is the first documented exploitation of CVE-2026-123890.
- 15 October 2026: GTIG discloses the BeyondTrust Remote Support zero-day CVE-2026-102764 used for initial access.
- 19 November 2026: Broadcom publishes VMSA-2026-0009 with the vCenter fix.
- 20 November 2026: GTIG and Mandiant publish the intrusion details.
Tradecraft
- Initial access and pivot: with the Remote Support appliance compromised, the actor planted two JSP webshells on an internal Linux appliance: SLIMSAVAGE (
ActiveSer.jsp, runs commands) and, about four hours later, CAGEMATCH (u.jsp, stages uploaded files). It ran nmap SYN scans for ports 443, 2012, 389, 5480 and 9080, then gained root by setting SUID on/bin/envthrough gdb. - Exploitation: tools were pulled with curl from the Remote Support appliance into
/tmp. BONESAW, a Go utility, exploits CVE-2026-123890 to dump the vmdir LMDB database (data.mdb), extract the STS SAML signing key, create a backdoor SSO administrator and give it Global Administrator rights. - Golden SAML: SAWSNAKE, a Go port of a public vCenter SAML login script, forges SAML assertions and administrator session cookies, which bypasses MFA.
- Persistence: BEARBONES, a backdoored Dropbear SSH server, listened first on TCP 53 and then on 33992, with a hardcoded bypass password and the banner
SSH-2.0-pulsesecure_23345. On vCenter the actor created a local adminsps-<redacted>@vsphere.local, turned SSH on through the VAMI API (PUT /rest/appliance/access/ssh), took the vCenter master symmetric key and the PostgreSQL password file, then turned SSH back off. LAZYBONES, a Go backdoor controlled through Slack, was installed as/usr/bin/vmtoolscson another appliance with a systemd service that restarts every 50 minutes. - ESXi and data theft: the actor logged in to hosts as
vpxuserand then over SSH as root, added its own key to root'sauthorized_keys, and usedvmfs_browser.pyto read guest VMDKs directly, extracting NTDS, SYSTEM, SECURITY and DNS data without ever touching the guest OS. The output was staged in a hidden.adirectory on a VMFS volume, packed aso.tar.gzand sent out through the Remote Support appliance. - Anti-forensics: separate reporting says the group also used CVE-2026-41709, an ESX insufficient-logging flaw that has been in CISA KEV since 28 October, to reduce audit visibility.
Indicators of Compromise
GTIG describes the IPs below as suspected obfuscation-network addresses. They are likely compromised or rented relays, so match on them for hunting and don't treat them as proof of attribution.
- 103.147.251[.]5, 103.190.38[.]3, 118.174.128[.]34, 118.174.128[.]36, 118.174.128[.]38
- 176.9.89[.]66, 185.71.15[.]109, 220.121.128[.]41, 222.108.77[.]44, 61.216.56[.]127, 81.45.89[.]43
- Files:
ActiveSer.jsp,u.jsp,/tmp/123(BONESAW),/tmp/sss(SAWSNAKE),/tmp/dbr(BEARBONES),/usr/bin/vmtoolscs(LAZYBONES),/tmp/123.key,/tmp/gdb_file,/tmp/123.rar - SSH banner
SSH-2.0-pulsesecure_23345on non-standard ports. TCP 33992 listeners.
Detection
- Search vCenter SSO for administrator accounts or machine accounts nobody created, especially
sps-prefixed local users and new Global Administrator assignments. - Alert on
PUT /rest/appliance/access/sshcalls to VAMI (port 5480), particularly when SSH is turned on and then off again shortly after. - Hunt Linux appliances for SUID set on
/bin/env, gdb attached to running processes, base64-pipedechocommands and curl downloads into/tmp. - Flag outbound connections from VCSA or infrastructure appliances to Slack API endpoints, and SSH services on unusual high ports.
- Check ESXi root
authorized_keys, hidden directories on VMFS volumes and unexpected SCP activity. GTIG has published six YARA hunting rules, one for each family.
# On the vCenter appliance (VCSA shell): defensive checks
find / -xdev -perm -4000 -name env 2>/dev/null
ss -tlnp | grep -E ':(53|33992)\b'
grep -rl 'vmtoolscs' /etc/systemd /usr/lib/systemd 2>/dev/null
# On each ESXi host
cat /etc/ssh/keys-root/authorized_keys
Recommended Actions
- Apply VMSA-2026-0009 now. There is no workaround.
- Restrict TCP 2012, 5480, 22 and 443 on vCenter to an allowlist of management hosts. Mandiant's VCSA hardening tool applies kernel-level iptables rules, egress filtering and syslog forwarding. Test it before rolling it out.
- If you run BeyondTrust Remote Support, confirm the BT26-05 fix is installed and assume compromise if it was exposed while unpatched.
- If you find any sign of compromise, treat it as a full identity incident. Rotate the vCenter STS signing certificate, SSO and service-account passwords and ESXi root credentials, and assume Active Directory secrets taken from guest disks are gone. That means resetting
krbtgttwice and rotating privileged accounts. - Forward vCenter and ESXi logs off-box, and keep management interfaces on an isolated network reachable only from privileged access workstations.
Analyst Assessment
This campaign repeats a pattern ARMORY CASTLE has used since 2023: break into an edge or security appliance, then move to infrastructure that EDR cannot see. Owning vCenter gives access to every VM disk, so the group could take domain secrets without running a single command inside a Windows guest. That defeats most endpoint detection. The BONESAW build date and its use against a host patched for the July vmdir bug point to deliberate research into the same component, so follow-on vCenter bugs are likely. Severity is Critical: the bug is unauthenticated, it has been exploited by a capable state-linked actor, and there is no workaround. Patching alone does not remove an attacker who is already inside, so hunting matters as much as the update.
