Apache mod_http2 CVE-2026-119618 Now Reported Exploited: Singapore CERT Warns of Active Attacks and a Public PoC — Update to 2.4.71 or Set Protocols http/1.1
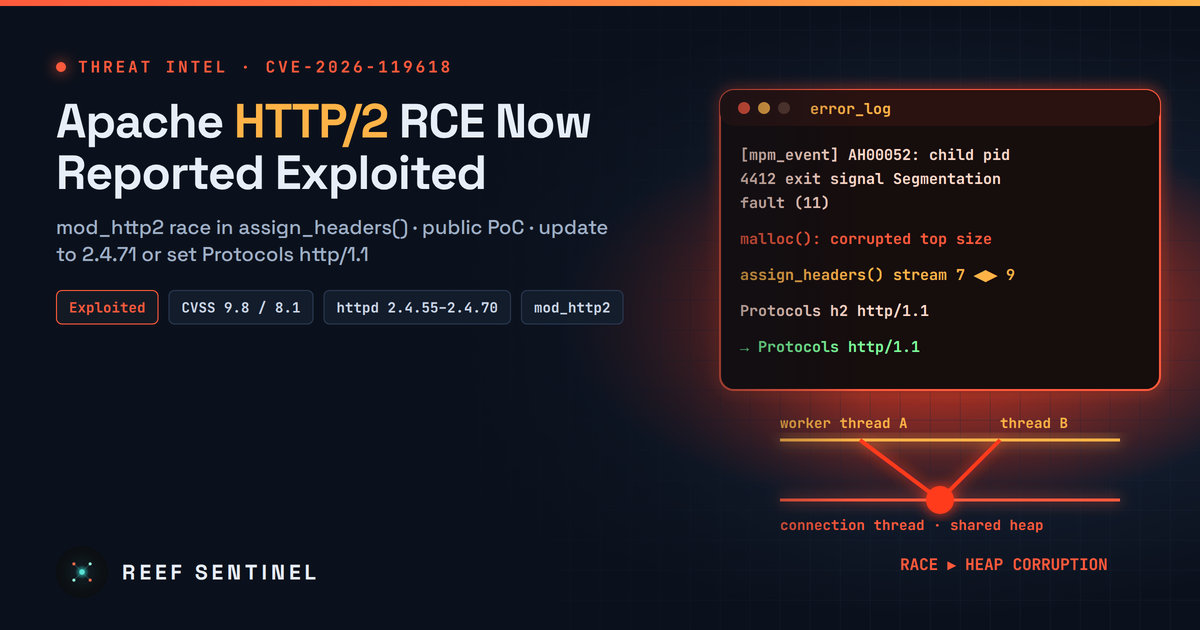
Singapore's CSA says the unauthenticated mod_http2 race-condition RCE in Apache HTTP Server 2.4.55–2.4.70 is reportedly being exploited with a public proof of concept, a week after the 2.4.71 fix.
Overview
A week after Apache released HTTP Server 2.4.71, the critical mod_http2 flaw it fixed, CVE-2026-119618, has moved from "patch soon" to "patch now". On 17 November 2026, Singapore's Cyber Security Agency (CSA) published alert AL-2026-164, "Active Exploitation of Vulnerability in Apache HTTP Server's mod_http2". It says the vulnerability is "reportedly being actively exploited, and a proof-of-concept exploit is publicly available", and tells organisations to update immediately.
We covered the patch release on 14 November. This is what has changed since then:
- A national CERT now reports exploitation in the wild.
- Repositories claiming to contain exploit code have been public since 12 November.
- Red Hat says public research has shown a reliable exploit against a default-configured server with mod_http2 enabled.
- Every major Linux distribution has now shipped fixed packages, so the remaining risk sits with servers that haven't installed them.
CSA has not said who is attacking, where the attacks were seen or how many servers were hit. When we checked on 18 November, CISA had not added the CVE to its Known Exploited Vulnerabilities (KEV) catalog. Treat the exploitation report as credible but not yet confirmed by other sources. Either way, internet-facing Apache servers that speak HTTP/2 should be patched or reconfigured today.
The Vulnerability
CVE-2026-119618 is a race condition (concurrent execution using a shared resource with improper synchronisation) in the assign_headers() function of mod_http2, the module that gives Apache HTTP/2 support. Red Hat describes it as a thread-safety flaw: one thread writes into memory that another thread owns. A worker thread handling a stream corrupts memory belonging to the connection thread through an allocator shared without a lock. The heap corruption can lead to remote code execution, and the attacker needs no login. They only have to send crafted, concurrent HTTP/2 requests.
Researchers who analysed the one-line fix (commit 824beab) say the trigger is a request that carries a Content-Type header but no Content-Length and no body. mod_http2 then writes a Content-Length: 0 header into the connection's shared header table instead of the stream's private copy. Any code that runs this way runs as the web server account (www-data, apache). Getting root would need a second, local flaw.
Affected and unaffected versions:
- Affected: Apache HTTP Server 2.4.55 through 2.4.70, and standalone mod_h2 2.0.8 through 2.0.42.
- Fixed: Apache HTTP Server 2.4.71, released 11 November 2026.
- Exposed only when mod_http2 is loaded and
h2orh2cappears in an activeProtocolsdirective. Servers that serve only HTTP/1.1 are not exposed. - Not affected: RHEL 8 and earlier, and mod_http2 builds older than 2.0.8.
- Distribution packages can keep an older version number while still containing the vulnerable code. Ubuntu 20.04 (2.4.41) and 22.04 (2.4.52) are both listed as affected in Ubuntu's notice.
Severity scores differ. Red Hat gives 9.8 (CVSS 3.1, low attack complexity). The CVE record carries 8.1 because it rates attack complexity as high, reflecting the race. Red Hat lowers its rating to Important on RHEL 9 and 10, because their mod_http2 packages give each HTTP/2 stream its own allocator, which makes exploitation much harder.
Timeline
- 26 October 2026: Anthropic's OSS Scanner reports the flaw to the Apache security team (ID ANT-2026-MAPKT6MZ).
- 3 November 2026: Anthony Weems and Simon Scannell of Google Cloud Vulnerability Research report it separately.
- 11 November 2026: Apache releases 2.4.71, which also fixes CVE-2026-106023 (mod_md NULL dereference, Important) and CVE-2026-109163 (mod_vhost_alias one-byte stack overwrite, Low). Debian publishes DSA-6620-1.
- 12 November 2026: Red Hat publishes bulletin RHSB-2026-017. Ubuntu publishes USN-9090-1. The first public repositories claiming exploit code appear.
- 14 November 2026: SUSE ships updates. The CVE record shows CISA's assessment of exploitation as "none".
- 17 November 2026: Singapore's CSA issues AL-2026-164, reporting active exploitation and a public proof of concept.
Tradecraft
No attack details have been published. Based on how the bug works, attackers are likely to:
- Scan for TLS services that offer
h2in ALPN and send Apache server banners. - Open many concurrent streams on one connection to win the race, which also crashes worker processes while they retry.
- After code runs as the web user, take the usual web-server route: a web shell in the document root, a downloader in
/tmpor/dev/shm, cryptominers, and theft of application secrets and TLS keys readable by that account.
Because winning the race is unreliable, failed attempts are likely to leave crashed Apache child processes in the logs. That makes them worth hunting for.
Detection
Find out whether a server is exposed:
apachectl -M 2>/dev/null | grep -i http2
grep -rn "^\s*Protocols" /etc/apache2/ /etc/httpd/ 2>/dev/null
curl -skI --http2 https://your-server.example/ | head -1   # "HTTP/2" = h2 negotiated
Hunt for signs of exploitation attempts and follow-on activity:
- Apache error log lines
AH00052/AH00051reporting child processes exiting onSegmentation fault (11),AbortedorBus error. - Kernel
segfaultmessages naminghttpdorapache2, and glibc errors such asmalloc(): corruptedordouble free or corruption. - Bursts of HTTP/2 requests from a single client in the minutes around those crashes. Adding
%{HTTP2}eand%{H2_STREAM_ID}eto yourLogFormatadds useful detail. - Shells, interpreters,
curlorwgetstarted byhttpd/apache2. New files in web roots,/tmp,/var/tmpor/dev/shm. New cron jobs or SSH keys for the web server account. Unexpected outbound connections from the server.
Check fixes against package changelogs or vendor advisory IDs, not version banners. Backported fixes make banner-based scanners unreliable in both directions.
Recommended Actions
- Patch now: upstream 2.4.71, Debian 2.4.71-1~deb13u1 (trixie, DSA-6620-1) or 2.4.71-1~deb12u1 (bookworm, DLA-4902-1), or Ubuntu USN-9090-1 packages (for example 2.4.58-1ubuntu8.19 on 24.04 and 2.4.52-1ubuntu4.27 on 22.04). On RHEL 9 and 10, apply the mod_http2 errata referenced in RHSB-2026-017. Restart httpd afterwards.
- If you can't patch yet, turn HTTP/2 off in the main configuration and in every virtual host, then restart:
Protocols http/1.1- Before turning it off, check that nothing depends on HTTP/2, such as gRPC back ends or h2c upgrade paths. A CDN or load balancer can keep serving HTTP/2 to users while talking HTTP/1.1 to the Apache origin.
- Rebuild container images based on
httpd, Debian or Ubuntu. Images pinned to old digests stay vulnerable. - Don't forget bundled Apache builds. Red Hat lists JBoss Core Services as affected, and appliances and control panels often ship their own httpd.
- Review logs back to at least 11 November. If you find signs of compromise, isolate the host, keep its memory and logs, rebuild it, and rotate application credentials, session secrets and TLS private keys.
Analyst Assessment
We rate this High to Critical for any organisation running internet-facing Apache with HTTP/2. Apache is one of the most widely deployed web servers, HTTP/2 is turned on by default in many distribution and hosting configurations, and the bug needs no login. The race condition, and the per-stream allocators on RHEL 9 and 10, make reliable exploitation harder. That explains the split between the 9.8 and 8.1 scores. But public exploit claims, Red Hat's statement that a reliable default-configuration exploit has been shown, and a national CERT's exploitation report together leave little room to wait.
The case also shows how quickly the window now closes. AI-assisted vulnerability discovery found the bug first, a second team found it within days, and the fix was public for less than a week before exploitation was reported. Expect broader scanning and a possible CISA KEV listing soon. Defenders should check their HTTP/2 exposure with real protocol probes, not module inventories.
