Fake Microsoft 365 Outage Notices Quote Real Incident EX1550543 to Phish Logins: 'Restore Held Mail in 24 Hours' Lures Run Through SendGrid Tracking to a Non-Microsoft Site
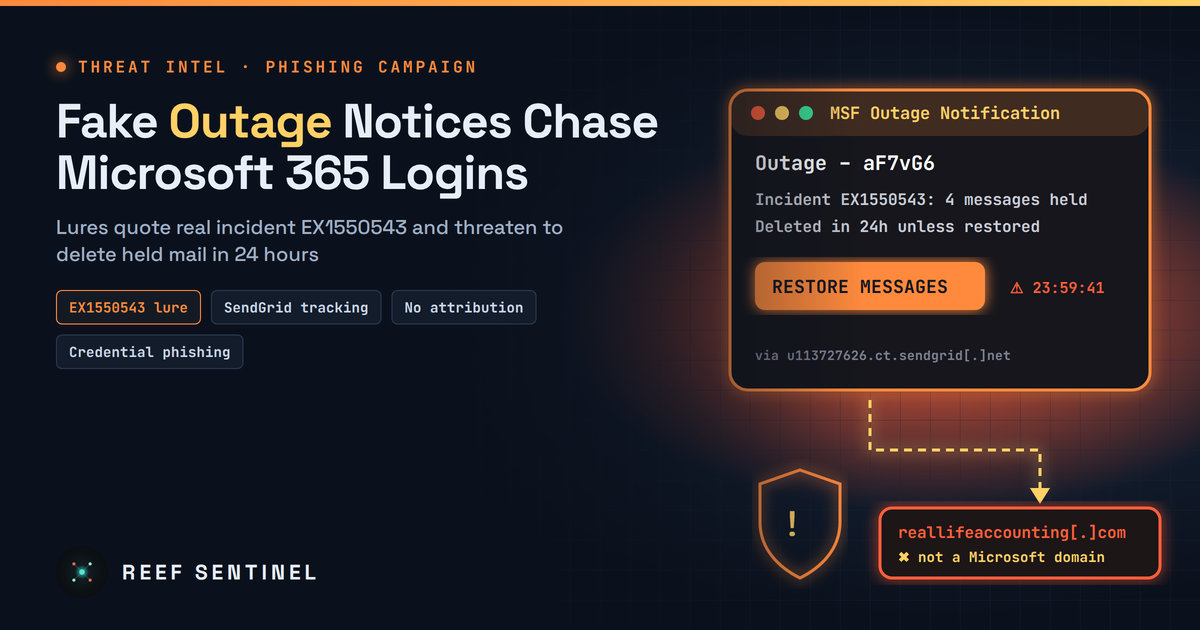
A day after the Microsoft 365 outage, phishing emails posing as Microsoft service-health alerts quoted the real incident number EX1550543 and sent users through tracked links to reallifeaccounting[.]com; here are the indicators, a fuller hunting query and response steps.
Overview
Less than a day after the long Microsoft 365 outage that took down Exchange Online and Outlook, phishing emails started pretending to be Microsoft's own "service health" messages about it. Microsoft Threat Intelligence says it saw the campaign on 13 November 2026. It aimed at organisations in many sectors and sent recipients through tracked links to a website that has nothing to do with Microsoft.
The bait is simple and believable: your mail was held during the outage, and it will be deleted in 24 hours unless you restore it. To look real, the emails quote the actual incident number, EX1550543, which administrators and many users had just watched for more than a day. Microsoft says the activity looks like credential phishing, but it has not confirmed that any credentials were stolen or any malware delivered. It has not named the group behind it, and it says its email protection is now blocking the campaign.
This is new information on top of our earlier outage coverage. Microsoft has also said the outage itself was "a technical issue not related to cyber or AI / agents". The company traced it to an earlier network capacity upgrade, and a later network change brought the fault to the surface. So the phishing came after the outage. It did not cause it.
The Campaign
The emails are built to look like real Microsoft 365 service notices:
- Subjects follow the pattern
Outage – <random token>, for exampleOutage – aF7vG6. Microsoft also listsStrengthen – Security <random>andRestore — 4 messages <random>. An "External" tag may come before the subject. - Display names use a three-letter prefix that looks like an organisation's short name, followed by "Outage Notification" or "Service Health". Examples are "MSF Outage Notification" and "AMZ Service Health".
- Brands named in the lures include Exchange Online, Outlook, Teams, SharePoint and Copilot. Microsoft listed all of these as possibly affected during the real incident.
- Calls to action are buttons labelled "RESTORE MESSAGES" or "TAKE ACTION". The 24-hour deletion warning is there to make people click before they think.
- Filter evasion: the message body also hides a fake email conversation that the reader does not see. Microsoft says this is likely meant to confuse content filters.
Delivery uses links only. Microsoft found no QR codes, no attachments apart from forwarded EML files, and no malware.
Timeline
- 12 November 2026: the Microsoft 365 outage begins. It affects Exchange Online mailboxes and Outlook, and may also affect Teams, SharePoint Online and Microsoft 365 Copilot. It is tracked as EX1550543.
- 13 November 2026: Microsoft marks EX1550543 resolved. On the same day, Microsoft Threat Intelligence sees the outage-themed phishing emails.
- 16 November 2026: Microsoft publishes its analysis with indicators and hunting queries. It confirms the outage was not a cyberattack, and says Defender is blocking the campaign.
Tradecraft
The sending infrastructure leans on legitimate bulk-email services so that each link is unique to its recipient:
- Three sender domains,
moments-notice[.]com,planetmaison[.]comandnewbooker[.]com, send the mail through bounce subdomains such asem4493[.]moments-notice[.]comandem[.]newbooker[.]com. - Clicks go first through per-recipient tracking hosts on a widely used email delivery service (
u113727626[.]ct[.]sendgrid[.]netand similar) and throughurl[.]newbooker[.]com. This lets the operator see who clicked, and the first hop looks harmless to URL scanners. - The chain ends at
reallifeaccounting[.]com, in some samples at/themelist0.html. Some messages instead point to throwaway.sbsdomains with outage-themed names:outagefixed[.]sbsandoutagerestored[.]sbs. - Tracking pixels are loaded from a separate host on a non-standard port (
162.120.17[.]69:8080) to confirm when an email has been opened.
Microsoft lists three MITRE ATT&CK techniques: T1566.002 (Spearphishing Link), T1036 (Masquerading) and T1204.001 (Malicious Link). Microsoft did not see the credential-capture page work, any post-compromise activity, or a named phishing kit. It is therefore unclear whether the final page collects passwords, relays MFA in real time, or does something else. Defenders should assume the worst case: a page that steals the session.
Indicators of Compromise
Sender and mail-from domains:
moments-notice[.]comem4493[.]moments-notice[.]complanetmaison[.]comnewbooker[.]comem[.]newbooker[.]com
Tracking and redirect hosts:
url[.]newbooker[.]comurl7489[.]newbooker[.]comu113727626[.]ct[.]sendgrid[.]netu118254266[.]ct[.]sendgrid[.]netu118250677[.]ct[.]sendgrid[.]net162.120.17[.]69:8080(per-recipient/t/v3…/px.pngresources)
Landing domains and URLs:
reallifeaccounting[.]comhxxps://reallifeaccounting[.]com/themelist0[.]htmloutagefixed[.]sbsoutagerestored[.]sbshxxps://outagerestored[.]sbs/topics_pxyk/themelist0[.]html
Microsoft warns against blocking the shared email-delivery service as a whole because of this campaign alone. Block the specific tracking subdomains and the landing domains instead.
Detection
Microsoft published three advanced hunting queries. They look for messages by sender domain or by the Outage – XXXXXX subject, for messages that contain the campaign URLs, and for user clicks on those URLs. Our review found that the published queries leave out some of the indicators in Microsoft's own list: planetmaison[.]com, both .sbs domains and two of the three tracking hosts. Add them back. The defensive example below covers the full list:
let senders = dynamic(["moments-notice.com","em4493.moments-notice.com","planetmaison.com","newbooker.com","em.newbooker.com"]);
let urls = dynamic(["reallifeaccounting.com","outagefixed.sbs","outagerestored.sbs","url.newbooker.com","url7489.newbooker.com",
  "u113727626.ct.sendgrid.net","u118254266.ct.sendgrid.net","u118250677.ct.sendgrid.net","162.120.17.69:8080"]);
EmailEvents
| where Timestamp > datetime(2026-11-12)
| where SenderFromDomain in~ (senders) or Subject matches regex @"(?i)Outage\s[–-]\s[A-Za-z0-9]{6}"
| project Timestamp, NetworkMessageId, RecipientEmailAddress, SenderFromAddress, SenderDisplayName, Subject, DeliveryAction, LatestDeliveryLocation
| union (UrlClickEvents | where Timestamp > datetime(2026-11-12) | where Url has_any (urls)
  | project Timestamp, NetworkMessageId, AccountUpn, ActionType, IsClickedThrough, IPAddress, Url)
Outside Defender, search proxy, DNS and secure web gateway logs for the landing domains, and for any outbound connection to port 8080 on the listed IP. Sender display names that end in "Outage Notification" or "Service Health" and come from outside your tenant are worth a mail-flow rule on their own.
Recommended Actions
- Search and purge. Find delivered copies by sender, subject and URL, then remove them with zero-hour auto purge or a manual purge. Remember that copies can sit in junk and other folders as well as the inbox.
- Find who clicked. For anyone with
IsClickedThrough = true, or a proxy hit on a landing domain, treat the account as possibly compromised. Reset the password, revoke sessions and refresh tokens, check MFA registrations, and look for new inbox or forwarding rules, mailbox delegates, OAuth consents and unusual sign-ins. - Block narrowly. Block the landing domains and the listed tracking subdomains at the mail gateway, the proxy and DNS.
- Tell users how real notices work. Microsoft does not ask users to "restore" held mail through a link to a third-party website. Service status lives in the Microsoft 365 admin center, and administrators, not end users, act on it. A short message to staff now is worth it, because outage-themed lures tend to keep coming for weeks after a high-profile incident.
- Harden identity. Move high-value users to phishing-resistant MFA (passkeys or FIDO2 security keys). Use Conditional Access with compliant-device or token-protection controls, and turn on Safe Links time-of-click checks for internal and external mail.
Analyst Assessment
The technical side is ordinary. The timing is the real threat. A real incident number, a real list of affected services, and a deadline built on real worry about lost mail make this lure better than generic "password expiring" emails. That is especially true for staff who spent 12 and 13 November without working email. Using legitimate bulk-email tracking hosts and disposable .sbs domains points to a financially motivated operator who can stand up new infrastructure quickly. We expect new sender and landing domains to appear even though the current ones are blocked.
Microsoft has confirmed no compromises and given no volume figures, so the scale is uncertain. Our confidence that this is credential phishing is moderate: it matches Microsoft's own assessment, but nobody has yet reported seeing the final page in action. The more lasting lesson concerns the next big cloud outage. Organisations should decide in advance how staff will receive real status updates, so that a convincing fake has nowhere to fit.
