Puppet Server CVE-2026-115731 Now Exploited: One Crafted Agent Report Gives Attackers Code Execution and the CA Signing Key — CISA Sets 1 December Deadline, Update to 2026.0.1, 2025.12.1 or 2023.8.13
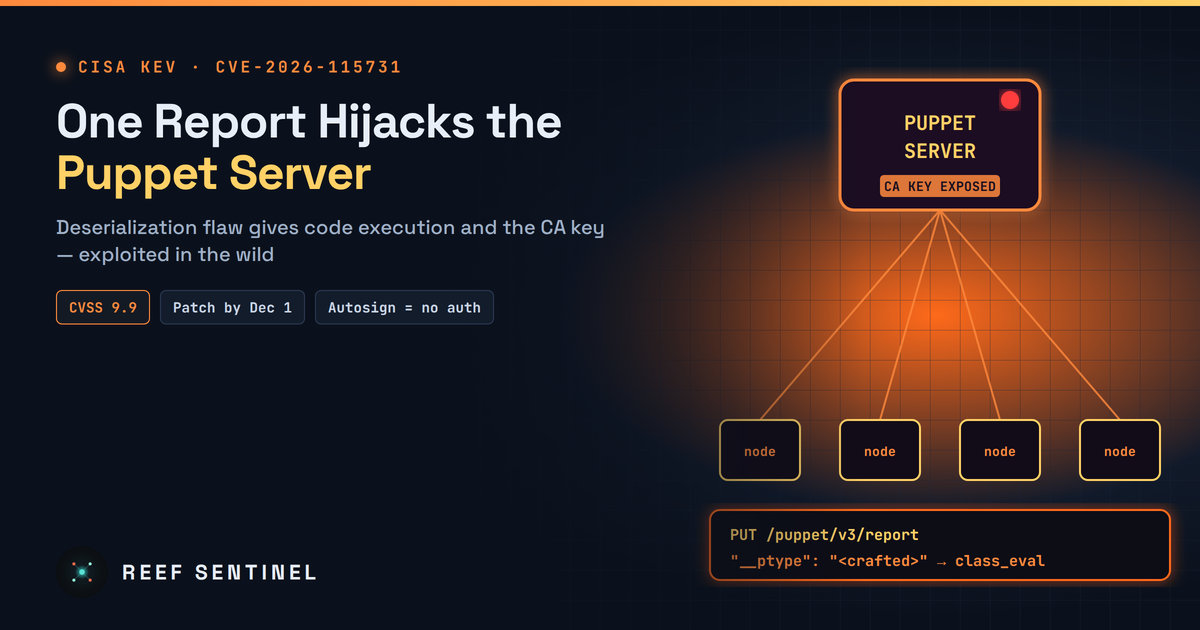
CISA has added Puppet's report deserialization flaw CVE-2026-115731 to its exploited list; any agent certificate (or open autosign) lets attackers run code on Puppet Server, steal the CA key and push changes to every managed node.
What Happened
On 17 November 2026 the US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-115731 to its Known Exploited Vulnerabilities (KEV) catalog, saying it has evidence the flaw is being exploited. The bug sits in Puppet Server, the central machine that tells every Puppet-managed computer how it should be configured. US federal civilian agencies must fix it by 1 December 2026.
The flaw was fixed two weeks ago. Perforce, which owns Puppet, and the maintainers of OpenVox, the community fork of Puppet, released patches on 3 November. The CVE record went live late that day, at 00:40 Mauritius time on 4 November (20:40 UTC on 3 November). Since then the original researcher's advisory, which includes a full proof-of-concept, has been public. Anyone with an unpatched Puppet server now faces a known exploit and confirmed attacks, and the CA key at the heart of their fleet is at stake.
CISA hasn't said who is exploiting the flaw or who has been hit, and no threat actor or campaign has been publicly linked to it. CISA's catalog lists ransomware use as "unknown".
Technical Details
Each time a Puppet agent finishes a configuration run, it sends a report back to the server with a PUT request to the /puppet/v3/report endpoint. The report is JSON and lists "events", one for each resource the agent changed.
The researcher behind the OpenVox advisory (credited as Alain from the security firm Neodyme) found that the server trusts too much of that JSON. The event data goes through Puppet's "rich data" converter (Puppet::Pops::Serialization::FromDataConverter), which reads a __ptype field set by the attacker, treats it as a Puppet type and creates an object of that type. A carefully built type can carry a Ruby method body in an annotation. When the type is turned into a real Ruby class, that code runs through class_eval.
In practice, a single crafted report makes Puppet Server run whatever Ruby code the attacker supplies. The code runs as the Puppet service user, on the server host or in its container.
Two conditions shape how serious this is:
- A certificate is needed, but it may not be much of a barrier. The attacker needs a client certificate signed by the Puppet certificate authority (CA). Any agent's certificate will do. If the CA is set to autosign certificate requests without strong checks, which is common in labs, cloud auto-scaling groups and quickly built environments, an attacker who can reach the server over the network can enrol a fake node and get a certificate. The attack then needs no prior access at all.
- The impact goes well beyond one server. According to the OpenVox advisory and Perforce, an attacker who controls Puppet Server can read the CA signing key, issue trusted certificates and change the code and configuration that every managed machine pulls on its next Puppet run. Red Hat notes that compromising the CA "could affect all downstream managed systems".
NVD and Red Hat score the flaw 9.9 (CVSS 3.1). Perforce and the OpenVox advisory score it 9.4 (CVSS 4.0). It is classified as CWE-502 (deserialization of untrusted data).
A Second Critical Bug in the Same Release
The same updates fix CVE-2026-115732 (CVSS 3.1 9.9, CVSS 4.0 9.0), a flaw in trapperkeeper-authorization, the library that reads Puppet's auth.conf rules. Plain-text rules were matched as if they were wildcards. As a result, a node with a certificate for a name like evil.target.example.com could pass checks meant for target.example.com and pose as that host. In Puppet Enterprise, the vendor says this can lead to CA administration and remote command execution on managed nodes. This second bug is not in the KEV catalog, but the same upgrade fixes both.
Who Is Affected
- Puppet Enterprise: 2023.8.0 to 2023.8.12, 2025.0.0 to 2025.12.0, and 2026.0.0.
- Puppet Core / open-source Puppet: 8.x before 8.22.2 and 9.x before 9.1.3.
- OpenVox: openvox-server up to 8.17.0 and 9.1.0, and openvox-agent up to 8.31.1 and 9.2.0.
- Red Hat Satellite: Red Hat lists its
puppetserverandopenvox-serverpackages as affected and rates the issue Critical, noting that the service accepts client reports over the network by default. - Distribution packages: the OpenVox maintainers say every known Puppet implementation is affected, including bundled and repackaged copies. They also warn that legacy open-source Puppet packages will get no further security updates.
Puppet is used widely in enterprise data centres, telecoms, universities and government for configuration management. Puppet servers usually sit deep inside the network, but they are often reachable from every managed host, and sometimes from the internet for cloud or remote fleets.
Patch Status
Fixed releases:
- Puppet Enterprise: 2023.8.13, 2025.12.1 or 2026.0.1.
- Puppet Core: 8.22.2 or 9.1.3.
- OpenVox: openvox-server and openvoxdb 8.18.0 or 9.2.0, and openvox-agent 8.32.0 or 9.3.0. For the OpenVoxDB container, use tag 8.18.0 or later.
Restart Puppet Server after upgrading so the fixed code actually loads.
What To Do Now
- Patch first. Upgrade to the fixed versions above and restart the server service. Treat the 1 December KEV deadline as an upper limit.
- Turn off or tighten autosign. Check
autosign.confor any policy-based autosign script. Naive autosign (trueor broad wildcards) turns this flaw into one that needs no prior access. - Limit who can reach port 8140. Only managed hosts should be able to talk to Puppet Server. Block it at the perimeter and between unrelated network segments.
- Hunt for signs of compromise. No public indicators of compromise have been published, so look for unusual behaviour. Check report submissions from unexpected or newly signed certnames. Look for new or unexplained certificates in the CA inventory, and for the Puppet service user starting shells or network tools. Also look for unexpected changes to Puppet code, Hiera data or catalogs.
- Re-check
auth.confafter upgrading. The OpenVox maintainers warn that custom rules may have relied on the old, faulty matching behaviour. - If you suspect compromise, assume the CA is gone. An attacker who has read the CA key can sign certificates of their own. Recovery means rebuilding the CA, re-issuing agent certificates and reviewing everything Puppet pushed during the exposure window.
# Check installed versions (run on the Puppet/OpenVox server)
puppetserver --version
puppet --version
# List signed agent certificates and look for unfamiliar names
puppetserver ca list --all
Why It Matters
Configuration management servers are among the most valuable targets on a network. Control one, and an attacker can push code to every machine it manages, using the trust the organisation itself built. CVE-2026-115731 joins a run of attacks on central management tools, including remote monitoring tools, hypervisor consoles and CI runners, where one weak point leads to the whole fleet.
The timeline is familiar too. A detailed, public proof-of-concept appeared on the day the patch was released, and two weeks later CISA confirmed exploitation. Teams that treat infrastructure tooling as "internal and low risk" are the ones still exposed.
