F5 BIG-IP: Six Critical TMM Overflows (CVSS 9.8) Let Unauthenticated Attackers Crash Traffic, Maybe Run Code, via iRules and APM — Hotfixes Only (CVE-2026-123637 + 5 More)
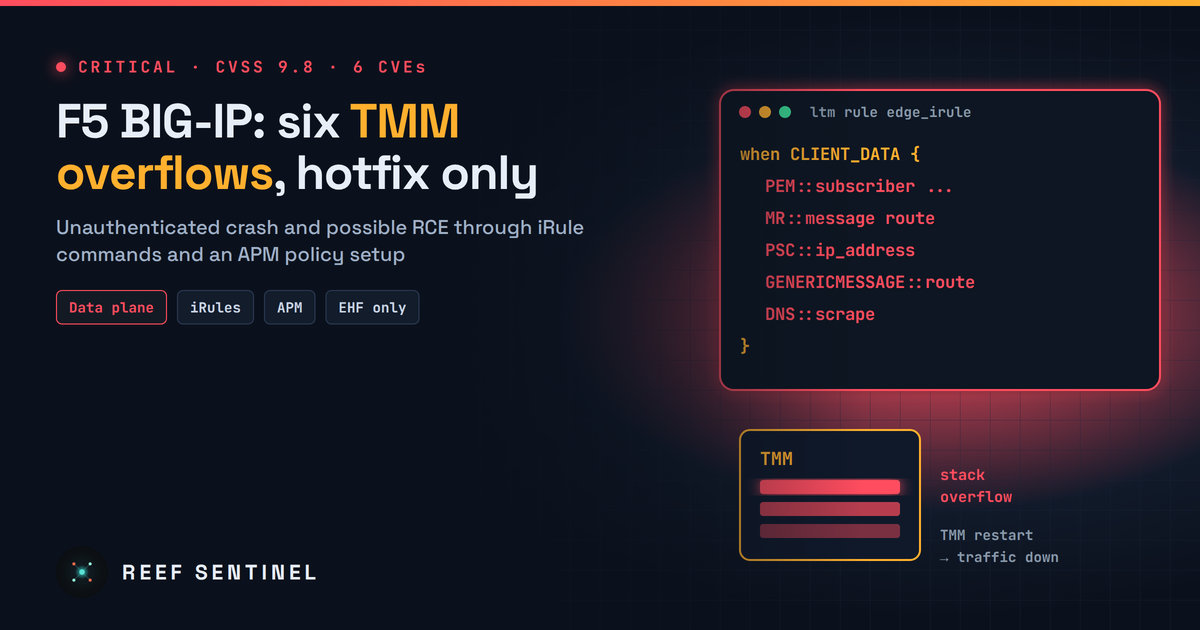
F5 disclosed six unauthenticated stack overflows in the BIG-IP, BIG-IP Next for Kubernetes and CNF data plane that crash TMM and may allow RCE when specific iRule commands or an APM per-request policy are in use, with only engineering hotfixes available so far.
F5 has disclosed six critical vulnerabilities in the BIG-IP data plane. Each one lets a remote attacker with no login crash the Traffic Management Microkernel (TMM), the process that carries all load-balanced traffic, and F5 says each "may lead to remote code execution". All six score 9.8 on CVSS v3.1 and 9.3 on CVSS v4.0. The catch for defenders: there is no regular fixed release yet. F5 is shipping engineering hotfixes, and you are only exposed if a virtual server uses one of a handful of specific iRule commands or one particular APM policy setup.
What Happened
F5 published the CVE records at 19:23 Mauritius time (15:23 UTC) on 18 November 2026, as part of a batch of 22 security advisories that also covered NGINX. All six are classed as CWE-121, a stack-based buffer overflow. They were found in the code that handles client traffic on a virtual server, triggered by what F5 calls "undisclosed requests".
The vendor says the flaws affect the data plane only: "There is no control plane exposure". In plain terms, the management interface is not the way in. The attack comes through the same virtual servers that carry your production traffic, and those are usually the parts of a BIG-IP that face the internet.
According to the vendor's advisories, four of the six were reported by an external security researcher and F5 found the other two itself. None of the advisories says the flaws have been exploited, and none of the six was in CISA's Known Exploited Vulnerabilities (KEV) catalog when this article was written.
The Six Flaws and Their Triggers
Each CVE needs a specific configuration. If a virtual server doesn't use the feature named below, that CVE doesn't affect it.
- CVE-2026-123637 (K000163937): BIG-IP APM is provisioned and a per-request policy that includes both the Client Information agent and Endpoint Security agents is applied to a virtual server. Affects BIG-IP APM only.
- CVE-2026-121805 (K000163946): an iRule that runs
PEM::subscriberon client traffic. Affects BIG-IP, BIG-IP Next for Kubernetes (BNK) and BIG-IP Next CNF. - CVE-2026-120292 (K000163940): an HTTP profile combined with an iRule that uses the
MR::message routecommand. Affects BIG-IP and BNK. - CVE-2026-120285 (K000163939): an HTTP profile combined with an iRule containing
PSC::ip_address. Affects BIG-IP, BNK and CNF. - CVE-2026-116953 (K000163941): an iRule that runs
GENERICMESSAGE::routeon client traffic. Affects BIG-IP and BNK. - CVE-2026-120722 (K000163945): an iRule that runs
DNS::scrapeon client traffic. The CVE record lists BIG-IP, BNK and CNF as affected. Researchers noted that F5's own advisory table listed CNF as not vulnerable at first, so check the current version of the advisory.
Technical Details
TMM is the heart of BIG-IP. It terminates connections, runs iRules and applies profiles. When TMM crashes, the device stops passing traffic until the process restarts. If it is targeted again and again, a single unauthenticated attacker could keep an application offline.
A stack-based overflow in TMM is serious beyond the crash. Overwriting data on the stack can, under the right conditions, redirect execution. That is why F5 scores these as full confidentiality, integrity and availability impact (AV:N/AC:L/PR:N/UI:N) even though its public wording says RCE is only possible. F5 has not published the request formats, and we include no exploit details here.
Past bugs show why the "data plane only" note is little comfort. CISA's KEV catalog already lists several earlier BIG-IP buffer overflows that attackers went on to exploit, among them a TMM overflow (CVE-2021-22991), a stack-based overflow (CVE-2025-53521, added 27 March 2026) and an APM heap overflow (CVE-2026-94127, added 22 September 2026, the day F5 disclosed it).
Who Is Affected
According to the CVE records, the affected branches are:
- BIG-IP: 17.1.x, 17.5.x and 21.1.x (for CVE-2026-123637, only systems with APM provisioned)
- BIG-IP Next for Kubernetes: 2.2.x, 2.3.x and 2.4.x
- BIG-IP Next CNF: 2.2.x, 2.3.x and 2.4.x (for CVE-2026-121805, CVE-2026-120285 and CVE-2026-120722)
F5 only assesses versions still under technical support. A version that has reached End of Technical Support and is missing from the tables has not been checked, which does not mean it is safe. The likeliest targets are service providers and carriers using PEM, Message Routing or generic message frameworks, DNS deployments that scrape responses in iRules, and enterprises using APM with endpoint posture checks for remote access.
Patch Status
There is no scheduled maintenance release that fixes these flaws. F5 is offering engineering hotfixes (EHFs), and warns that these "do not undergo the extensive QA assessment of scheduled software releases". If a system already runs a custom hotfix, F5 support has to build a new one that combines both.
The vendor's advisories list these hotfixes for Kubernetes and CNF:
- BNK: BNK-2.4.2-EHF1, BNK-2.3.4-EHF1 and BNK-2.2.5-EHF1
- CNF (for CVE-2026-121805 and CVE-2026-120285): CNF-2.4.2-EHF1, CNF-2.3.4-EHF1 and CNF-2.2.5-EHF1
For classic BIG-IP, request the hotfix for your branch through the advisory pages or F5 support. The same batch also fixed six lower-rated flaws in iControl SOAP, iControl REST, APM SAML and SSL Orchestrator. The regular fixes for those are in BIG-IP 21.1.0.3, 17.5.1.10 and 17.1.3.6, but those releases do not fix the six critical TMM bugs.
What To Do Now
Find out whether any of the trigger commands are in use. Run these from the BIG-IP shell. They only read the configuration:
# Show the running version
tmsh show sys version

# Find iRules (all partitions) that use any of the vulnerable commands
grep -nE 'PEM::subscriber|MR::message|PSC::ip_address|GENERICMESSAGE::route|DNS::scrape' \
  /config/bigip.conf /config/partitions/*/bigip.conf 2>/dev/null

# List which iRules are attached to which virtual servers
tmsh list ltm virtual all-properties | grep -E '^ltm virtual|rules' - If nothing matches and you don't use the APM setup described above, your exposure to these six CVEs is low. Still plan the next maintenance release.
- If an iRule matches, check whether it is attached to an internet-facing virtual server. Where the business can manage without it, detach it or rewrite the logic without that command until the hotfix is installed. Researchers point out that avoiding the command is the only interim measure F5 has described.
- For APM, review Access › Profiles/Policies › Per-Request Policies to see whether any policy combines the Client Information agent with Endpoint Security agents, and prioritise those systems.
- Open a case with F5 support for the EHF matching your exact version. Test it in staging, because hotfixes get less QA than regular releases.
- Monitor for TMM restarts and core files. Unexpected TMM cores in
/var/coreor restart messages in/var/log/ltmmay be the first sign that someone is probing these flaws.
Why It Matters
BIG-IP devices sit in front of banking portals, government services, VPNs and carrier networks. A pre-authentication bug in the traffic path can take a whole application offline, and that is the best case. Attackers have repeatedly turned F5 overflows into working exploits within days of disclosure, sometimes on the same day. With hotfixes only and narrow, configuration-dependent triggers, the main risk is that teams decide they are not affected without checking. An hour spent searching your iRules today is cheaper than an emergency hotfix after the first proof of concept appears.
