XaocMail ClickFix Campaign Hides Phantom53 Commands in DNS-over-HTTPS Lookups, Then Loads Havoc on Chosen Victims — Researchers Say the Toolkit Was Built With Claude Code
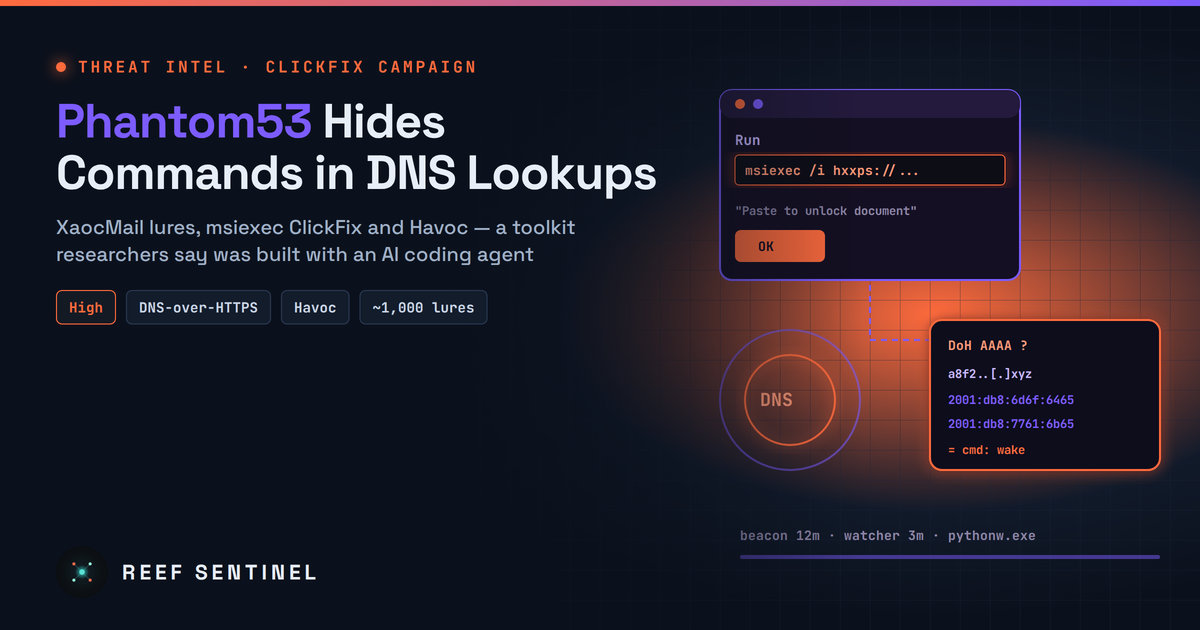
A Russian-speaking actor's ClickFix operation has pushed almost 1,000 personalised fake document pages since August 2026, installing a Python-based Phantom53 implant that takes commands through encrypted DNS and steals passwords, SSH keys and AI coding tool secrets.
Overview
Security researchers have documented an active phishing operation run by a Russian-speaking threat actor that chains three tools together: XaocMail, a self-hosted phishing platform (the name comes from the Russian word for "chaos"); Phantom53, a custom remote-control framework that hides its command traffic inside DNS lookups; and the open-source Havoc post-exploitation framework, which is loaded only on victims the operators choose by hand.
The campaign went live in August 2026 and is still running. Researchers found almost 1,000 personalised fake document-sharing pages, most aimed at Latin America (led by Brazil and Peru), with more in India, Indonesia and Spain. The technology and IT sector is slightly ahead of finance, education, government, logistics and manufacturing among the targets. Researchers warn that a compromised IT company could become a route into its own customers.
What makes this report stand out is the build process. The researchers recovered material from the operators' workspace that, they say, shows the toolkit was developed and tested with help from Anthropic's Claude Code. That includes a .claude/ configuration folder, 143 numbered task files and a 117 KB architecture document. The tradecraft itself is not new, but it is well put together, and this is another real-world sign that AI coding agents are cutting the time it takes criminals to build working malware.
The Campaign
The attack starts with an email posing as a document-sharing notice from Google Docs, Adobe Acrobat, Office365 or a "SecuredDocs" service. XaocMail personalises each lure with the recipient's name, the sender's name, the company name and the document type, and gives every victim a unique 8-character link ID.
The link opens a page hosted on Cloudflare Workers showing a blurred document. To "unlock" it, the victim is told to press Win+R and paste a command. This is the ClickFix technique (MITRE ATT&CK T1204.004, Malicious Copy and Paste). The pasted command can use PowerShell, mshta or msiexec; researchers say the msiexec route is the newest and preferred one. When the command runs, the page removes the blur so the victim sees what looks like a normal document.
The MSI pretends to be Visual Studio Tools, Python or Node.js. It installs a private Python 3.11 runtime into a random folder and drops the Phantom53 components as compiled .pyd modules named to look like common Python libraries such as OpenCV, NumPy, PIL or lxml.
Timeline
- October 2025: Preparation begins, including malware testing and the Cloudflare infrastructure.
- First half of 2026: Lures are refined and the implant is hardened through several versions. Earlier builds used a GitHub-hosted
gistfile1.txt/update.zipthat sideloaded a maliciouslibcurl.dllthroughGUP.exe. - August 2026: The operation launches at scale.
- 17 November 2026: The research is published; the campaign is described as still active.
Tradecraft
Persistence. Two scheduled tasks run pythonw.exe so no console window appears. They are named after legitimate updaters for OneDrive, Edge, Defender and Adobe (reports cite names such as OneDriveSyncTask). The beacon (beacon.pyd) runs every 12 minutes; the watcher (watcher.pyd) runs every 3 minutes.
Sandbox checks and profiling. The beacon delays contact on young or idle systems, then sends the computer name, user name, running processes and installed security tools to the operators. A two-step cookie handshake blocks replayed sessions.
DNS command channel. Phantom53 sends its queries through DNS-over-HTTPS to the public resolvers of Google, Cloudflare and ControlD, and the replies carry commands encoded inside IPv6 (AAAA) answers. If DoH is blocked, it falls back to plain DNS on UDP port 53. A weekly, SHA256-based domain generation algorithm produces fallback .xyz domains, and each candidate is checked with an Ed25519 signature, so defenders cannot take over the channel by registering a predicted domain.
Hands-on stage. When an operator selects a victim, a "wake" command makes the watcher decrypt an AES-256-GCM Havoc Demon blob (demon.dat) and load it reflectively into memory. Operator shortcuts include running PowerShell, changing the beacon interval, moving domains, wiping the implant, installing the Level RMM tool, bypassing UAC via fodhelper and guessing the local Administrator password over SMB.
What it steals. Password-manager extensions, VPN and OpenVPN configurations, Chrome data, SSH keys, GitHub CLI tokens, crypto wallets and seed phrases, WhatsApp, Telegram and Signal data, and secrets for AI coding tools (Claude Code, Codex, Gemini CLI and Cursor).
AI-assisted development. Researchers describe a Russian-language prompt that told a Claude agent to install a test MSI on a virtual machine named "NoAV", wait for the beacon and run a cleanup script, framed as an "authorized red team" exercise to keep the agent working.
Indicators of Compromise
A selection of published indicators (defanged):
185.224.132[.]148— XaocMail landing page, backend and DNS server145.63.138[.]67— exfiltration (port 8125) and Havoc C2162.252.198[.]204,162.252.199[.]92— operator servers91.132.93[.]251— reverse SOCKS / WebSocket relaysecuredoc.makeneg458.workers[.]dev,securedoc.mesuttgulerr573.workers[.]dev— ClickFix lure pagesdns.timesyncserver-312453[.]com,sync-node-serv[.]com,dns.cdn-syncnode-server[.]com— C2a8f2aac37385[.]xyz,kfkwrfdd[.]xyz,544504d7fe1e[.]xyz— Phantom53 C2bestutyresdomaonupder[.]com,bestutyresdomaonupder[.]top— relay domains- SHA256
4f656834e545c0b44922ce6d8952989c8c0859d8ae8b1f117c06ab07b047e2b4—beacon.pyd - SHA256
8ebb2bf61b48ae7abdcd674413bebd79b30ddd945854e175ba60d56c0a3adf54—watcher.pyd - SHA256
bceeb2d54b6a756c73a3e06617e9e95ad4d8e53da47639bcd6ef3cae98c6da6d— HTA payload - SHA256
79a4cb73983a1facb5db09f1a20cec6e58d91a93044a78aa3ba32ab2190284ed— PowerShell payload
Because the operators rotate Workers subdomains and use a DGA, these indicators will go stale. Behaviour-based detection matters more.
Detection
- Alert on
msiexec.exe,mshta.exeorpowershell.exestarted byexplorer.exewith a URL on its command line (the Run dialog pattern), especially*.workers.dev. - Alert on
pythonw.exelaunched by Task Scheduler from a user'sAppDatafolder, and on any Python runtime installed outside standard paths. - Flag endpoint processes other than browsers talking to DoH resolvers (
dns.google,cloudflare-dns.com, ControlD), and bursts of AAAA lookups for random-looking.xyzdomains. - Review new scheduled tasks named after OneDrive, Edge, Defender or Adobe updaters whose action points to
pythonw.exe. - Hunt for
.pydfiles named after OpenCV, NumPy, PIL or lxml in unusual locations, and for unexpected Level RMM installs.
A quick check for suspicious tasks on a Windows host:
Get-ScheduledTask | Where-Object { $_.Actions.Execute -match 'pythonw' } |
  Select-Object TaskName, TaskPath, @{n='Action';e={$_.Actions.Execute + ' ' + $_.Actions.Arguments}}
Recommended Actions
- Block the published IPs and domains, and search DNS, proxy and EDR logs back to August 2026.
- Restrict the Win+R Run dialog for standard users through Group Policy where your business allows it, and block
mshta.exewith application control. - Route all DNS through your own resolvers and block or inspect outbound DoH to public resolvers from endpoints.
- Teach staff a simple rule: no legitimate website will ever ask you to paste a command into Windows.
- If a host is affected, rotate everything it could reach: password-manager vaults, SSH keys, GitHub tokens, VPN credentials and AI coding tool API keys.
- IT service providers should check technician workstations first, given the risk to downstream customers.
Analyst Assessment
We rate this campaign High. ClickFix keeps working because the victim runs the attacker's command themselves, which slips past many email and web filters. Hiding commands inside encrypted DNS lookups to big public resolvers removes another common detection point. The careful design — signed DGA domains, replay protection, in-memory Havoc and a hand-picked second stage — points to an operator who wants to stay quiet and choose valuable targets.
The AI angle should be read carefully. Researchers' evidence shows an AI coding agent helped write and test the toolkit, but none of the techniques are new. The real change is speed and polish: a small team can now ship a multi-component framework that would once have needed more people. The theft of AI coding tool secrets is also worth noting, because stolen agent keys and tokens can lead to source code and build pipelines. Defenders should expect more campaigns like this.
Sources
- Russian-Speaking Hackers Use AI-Assisted Malware and ClickFix Attacks to Target Windows Users (Cyber Security News)
- Hackers Use Claude Code to Develop Phantom53 Malware for ClickFix Attacks (GBHackers)
- User Execution: Malicious Copy and Paste, T1204.004 (MITRE ATT&CK)
- Application Layer Protocol: DNS, T1071.004 (MITRE ATT&CK)
