Fireworks AI Breach Reaches Uber: Drivers' Names and Licence Numbers Stolen From an AI Vendor Account — State Filings List 7,870+ Drivers in Three States Alone
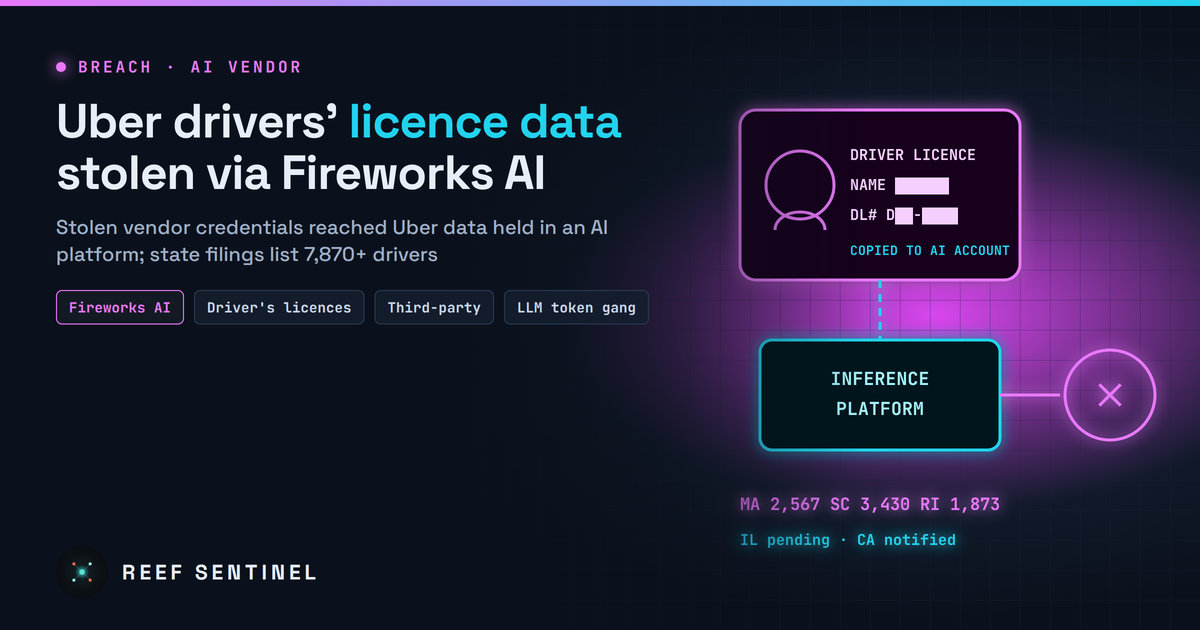
Uber is notifying US drivers that stolen Fireworks AI credentials exposed licence data it held with the AI provider, the latest downstream victim of a breach Fireworks blames on a gang that sells LLM access tokens.
Overview
Uber is notifying US drivers that their names and driver's licence information were stolen in a breach at Fireworks AI, a company that gives developers hosted access to open AI models. Uber's statement attributes the notices to "a security incident impacting one of our third-party vendors, Fireworks.ai," which had access to some Uber data.
What is new: we have already covered the Fireworks AI breach itself and the downstream compromise of Cursor. Uber is a new downstream victim, and this time the stolen data is regulated identity data, not code or model assets. Breach notices filed this week with US state attorneys general list:
- 2,567 Massachusetts residents
- 3,430 South Carolina residents
- 1,873 Rhode Island residents
- Illinois residents (count pending)
- California drivers (no count given)
Uber has not published a national total. The roughly 7,870 figure seen in some coverage is just the three state counts added together, so the real number is likely higher.
The Incident
According to Uber's notices, Fireworks told Uber on 9 October 2026 that unauthorised parties had compromised Fireworks' internal credentials. Those credentials were then used to reach Uber data held in Uber's Fireworks environment. Fireworks has confirmed "a security issue involving unauthorized access to some of its systems" that affected customer data. It blames a financially motivated group that sells stolen access tokens for large language models. No group has publicly claimed the Uber data theft.
The wider Fireworks incident has already hit several customers. Customer billing data, private AI datasets, secrets and partial model weights were reported stolen. Notion has confirmed it was affected. Cursor has said a stolen Fireworks key led to its own breach and to a backdoored extension being pushed through its marketplace.
Uber says it has cut its data connections to the provider and opened an investigation. It has not explained why driver's licence data was stored in a third-party AI inference account, listed every data type taken, or said whether it will keep using Fireworks. It reports no confirmed misuse of driver data so far. This is Uber's second known breach of 2026, after an earlier incident at Uber Freight that an extortion gang claimed.
Timeline
All times are Mauritius time (UTC+4), with UTC in brackets.
- Early October 2026: Attackers compromise Fireworks AI internal credentials and access customer environments
- 9 October 2026: Fireworks tells Uber that its internal credentials were compromised
- October 2026: Fireworks discloses its own breach. Customer billing data and private datasets are reported taken
- Week of 9 November 2026: Uber files breach notices with several US state attorneys general and begins notifying drivers
- 13 November 2026: Uber publicly names Fireworks AI as the vendor involved
Tradecraft
- Vendor pivot: once inside the AI provider, the attackers used its internal credentials to reach the data that customers had placed with it, the same pattern seen at Cursor and Notion.
- LLM-access economy: Fireworks attributes the breach to a group that trades in stolen LLM access tokens. This is the same underground market behind "LLMjacking", where stolen keys are resold as cheap model access. In this case, access to an AI platform also exposed whatever data customers had sent to it.
- Data gravity in AI pipelines: to fine-tune, evaluate or run inference on real workflows, companies copy production data, sometimes including personal identifiers, into third-party AI environments. Those copies often get weaker governance than the systems of record.
Detection
No indicators of compromise have been published. Organisations that used Fireworks AI, or any hosted inference or fine-tuning provider, should:
- Rotate every API key, service token and webhook secret shared with the provider. Check the provider's audit logs for access from unfamiliar IP addresses since 1 October 2026.
- List the datasets, fine-tuning files, prompts and logs stored in the provider's environment. Identify any that contain personal data, credentials or secrets.
- Watch your own systems for use of credentials that may have been held in, or exposed through, that environment.
Recommended Actions
- Affected drivers: read the notice letter carefully and use any identity protection offered. Consider a credit freeze with the US credit bureaus. Expect phishing that quotes real licence numbers or Uber account details. Uber will not ask for your password or full ID by text or phone.
- Security and data teams: treat AI vendors as data processors. Minimise or tokenise identifiers such as licence numbers before sending data to model providers. Put retention limits on uploaded datasets and logs.
- Add AI platforms to your third-party risk register, with breach-notification terms, key-rotation runbooks and the ability to delete data quickly.
- Don't use long-lived static API keys for AI providers. Prefer short-lived, scoped credentials where the provider supports them.
Analyst Assessment
The Uber notices show that the Fireworks AI breach is still spreading downstream, and that the damage goes beyond intellectual property to regulated personal data. The breach began with a gang that monetises LLM access, but every customer that stored sensitive data in the provider's environment inherited the risk.
Expect more downstream notifications from Fireworks customers in the coming weeks, and more regulatory interest in why identity documents were sitting in AI inference accounts. For defenders, AI vendors now need the same data-minimisation and vendor-risk discipline as any other processor of customer data.
