Operation CloudFire: Google Calendar Invites From Trusted Senders Steal Live Google Sessions Past MFA — 8,570 Compromised Accounts Sent Lures, 897 Phishing Domains Taken Down
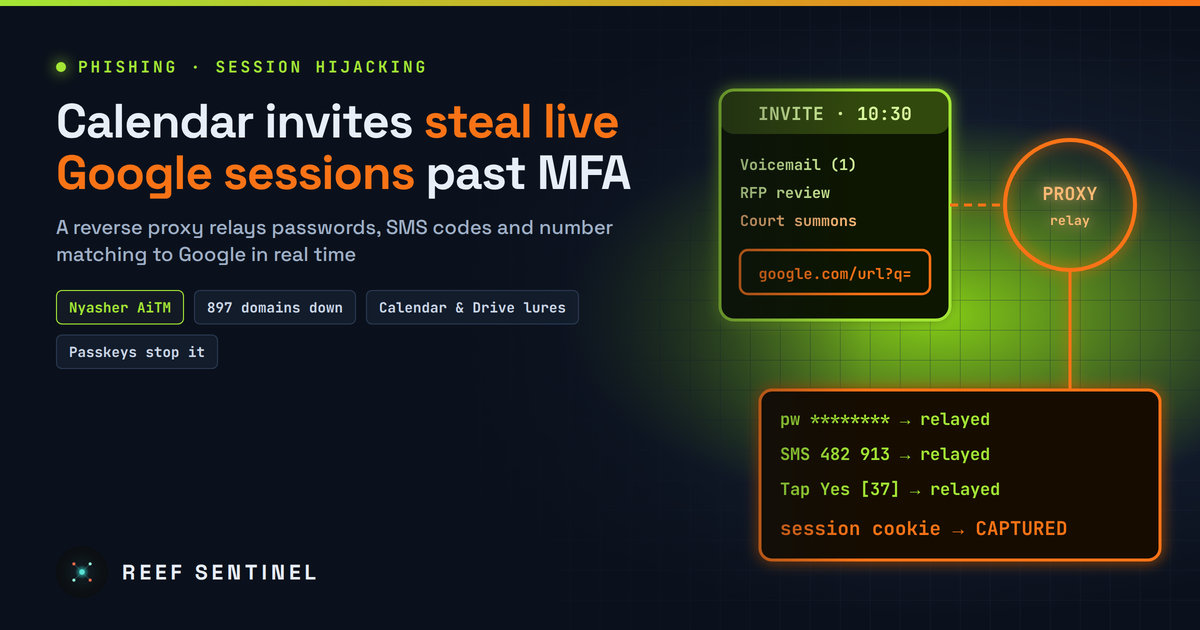
A Nyasher-powered reverse-proxy campaign running since mid-August uses Google's own redirector and browser-built login pages to relay passwords, SMS codes and number matching, then reuses each victim's account to phish their contacts.
Overview
Since mid-August 2026, a phishing operation has been stealing live, authenticated Google sessions from corporate users. Its lures are Google Calendar invites, and later Google Drive share notifications. They arrive from real, previously trusted accounts. Victims are passed through a reverse proxy placed in front of Google's genuine sign-in page. The operator relays the password and the second factor to Google in real time and keeps the resulting session.
Email security researchers ran a takedown effort they call Operation CloudFire and published fresh details this week. In one month, from a subset of customers who agreed to share data, they counted:
- 68,676 campaign messages blocked
- 2,112 unique malicious URLs analysed
- 897 lure domains taken down
- 8,570 compromised sender addresses across 6,354 root domains
The real totals are likely higher.
The Campaign
The invites use pretexts that make people act fast: voicemail notices, RFP or RFI requests, court summonses and missed-payment alerts. Many are sent by BCC. They usually come from organisations the recipient already corresponds with, because each victim's account is used to mail its own saved contacts. That is how the campaign spreads from one company to its partners and suppliers.
The link chain is built to pass every reputation check:
- Most links start with Google's own
/urlredirector, with the real destination hidden in a query parameter. Other waves usedshare.google, Google Drive file links and, in one variant, Intuit transaction notification links. - Next comes a Cloudflare Turnstile challenge, sometimes the genuine widget, which blocks automated scanners.
- Only after the challenge does JavaScript in the victim's browser build the credential page. Crawlers and proxy logs never see a static phishing page.
The capture page is a live reverse proxy run with Nyasher, a phishing framework that has been publicly documented since February 2026 after researchers found a hard-coded key in its JavaScript. Because the real Google page is relayed, the operator can pass along:
- SMS one-time codes
- Authenticator app codes
- Google's "Tap Yes" number-matching prompts
- Phone-based account recovery
None of these stopped session capture. The operator also built an unfinished Microsoft 365 branch alongside the Google code, so a switch of target is a real possibility.
Timeline
All times are Mauritius time (UTC+4), with UTC in brackets.
- February 2026: Nyasher framework publicly documented
- Mid-August 2026: Calendar-invite session-hijacking waves begin against corporate Google Workspace users
- September 2026: Researchers start reporting gateway and backend infrastructure to Cloudflare's abuse team. Cloudflare confirms the pages and places phishing warnings in front of them
- Late October 2026: Lures shift from calendar invites to Google Drive file and document share invitations. Activity begins to scatter
- 12 November 2026: Updated technical details and the CloudFire takedown figures are published
Tradecraft
- Disposable infrastructure: lure domains were registered across several registrars, often only days before use. Receiving endpoints were staged one to twenty days ahead of each wave. In one case, a wildcard TLS certificate was issued 46 minutes before its domain was even registered.
- Living off trust: compromised senders, Google-owned first hops and a real CAPTCHA made the messages look clean to gateways built for ordinary email.
- Working hours: sending followed US business hours, so the messages blended into normal traffic.
- Post-compromise: with a live session the operator can read Gmail and Drive, grant OAuth access to applications in the victim's name and send new invites to the victim's contacts. A password reset alone may not end that access.
Detection
The researchers did not publish domain or IP indicators in their public write-up, so detection has to rely on behaviour:
- Treat calendar invites as their own threat surface. Flag invites from external senders that contain links, especially ones routed through
google.com/url?q=orshare.google, or that carry urgent payment, legal or voicemail themes. - In Google Workspace audit logs, look for a successful login from an unfamiliar IP address or ASN shortly after the user received an external invite. A second session on a different network while the user's normal session is still active is a strong signal.
- Review OAuth token audit events for new third-party app grants. Look for bursts of outbound calendar invites or Drive shares from a single account.
# Example using the open-source GAM tool for Google Workspace (adjust dates)
gam report login start -7d                    # recent login events with IP addresses
gam report token start -7d                    # OAuth grants and revocations
gam user <user@example.com> show tokens       # apps currently holding tokens for a user
Recommended Actions
- Move privileged and high-risk users to phishing-resistant authentication: passkeys or FIDO2 security keys. These are bound to the real origin and cannot be relayed through a proxy.
- If an account may be affected, revoke all active sessions, remove suspicious OAuth grants, reset the password and check mail forwarding rules and Drive sharing. The researchers advise being able to do all of this within about an hour.
- Consider setting Google Calendar so that invites from unknown external senders are not added to calendars automatically.
- Report lure infrastructure to hosting and abuse providers. Interstitial warnings measurably slowed this operator.
- Tell staff that a familiar sender is not proof of safety, and that a Google sign-in prompt reached from a calendar invite deserves extra suspicion.
Analyst Assessment
This campaign shows that adversary-in-the-middle phishing has matured. It combines trusted senders, Google-owned redirectors and pages built only in the browser, which defeats the reputation, link-analysis and crawling controls most organisations depend on. SMS codes, app codes and number matching all fell to live relay.
The takedown raised the operator's costs, but rebuilding is cheap, the framework is public and a Microsoft 365 module is already half-built. Expect the same playbook to return under a different brand and lure. Phishing-resistant MFA plus fast session and OAuth revocation is the durable answer.
