BluePhishing: One Consent Click on a Malicious Entra Agent Blueprint Lets Attackers Spawn Up to 250 AI Agent Identities With Permissions Admins Can't See
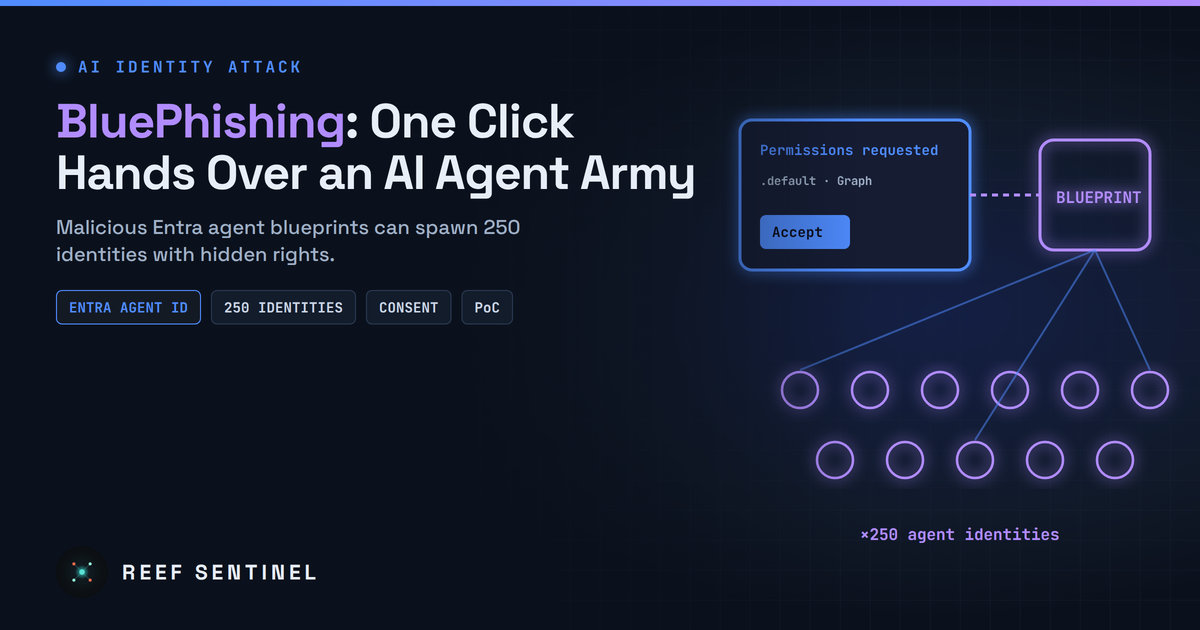
Researchers show how consent to a malicious third-party Microsoft Entra agent blueprint gives attackers an irrevocable right to create up to 250 agent identities whose inherited permissions are invisible in the portal and Graph.
Overview
Security researchers have published BluePhishing, a proof-of-concept attack against Microsoft Entra Agent ID, the identity layer Microsoft is rolling out for AI agents. A user who approves one consent prompt for a malicious third-party agent blueprint gives the attacker a foothold in their tenant. That foothold can create up to 250 agent identities, which hold permissions that admins cannot see in the Entra portal or through Microsoft Graph.
No in-the-wild use has been reported, and the researchers notified Microsoft before publishing on 9 November 2026. It matters now because, under Microsoft 365 Message Center post MC1506733, ordinary Entra users can start creating agent blueprints in November 2026. Consent to agent blueprints is about to become an everyday prompt.
The Vulnerability
This is a design-level consent-phishing technique, not a CVE. Classic OAuth consent phishing gives an attacker one service principal. BluePhishing produces a blueprint principal that automatically receives the application permission AgentIdentity.CreateAsManager, which cannot be revoked from the principal. That permission lets the attacker create new agent identities linked to the blueprint, each one inheriting the blueprint's configured permissions.
The researchers found that inherited permissions do not appear in the Entra portal or Graph. They are only visible inside the access tokens at runtime, which makes them hard to audit. Silent inheritance was observed for user-consented delegated permissions. Admin-consented permissions were labelled "inherited from parent".
Timeline
- November 2026: per MC1506733, default Entra users can begin creating agent blueprints.
- Before publication: the researchers report their findings to Microsoft.
- 9 November 2026: BluePhishing is published as research, with no observed in-the-wild abuse.
Tradecraft
The attack chain, at a high level:
- The attacker creates a multi-tenant agent blueprint in their own tenant (
signInAudienceset toAzureADMultipleOrgsthrough Graph or PowerShell, since the portal does not allow it). They add a client secret and the permissions they want. - They send the target a link to the admin consent endpoint with
scope=https://graph.microsoft.com/.default, which grants everything listed in the blueprint's required resource access. - The victim clicks Accept, and a blueprint principal is created in the victim's tenant.
- The attacker requests an app-only token for the victim tenant using the blueprint's credentials.
- They create agent identities through Graph, naming a victim user as the identity's "sponsor".
- The agent identities obtain Graph tokens with the inherited permissions. In testing,
User.Read.AllandGroup.Read.Allwere enough to run a post-exploitation toolkit for directory reconnaissance.
The attacker only needs the victim tenant ID and a user's object ID, and the researchers note both can be gathered through unauthenticated endpoints. Microsoft already blocks some high-risk Graph permissions, such as User.ReadWrite.All, for agents, which limits but does not remove the impact.
Indicators of Compromise
No campaign indicators have been published, because no in-the-wild abuse has been observed. One useful hunting property: a malicious blueprint has the same application ID in every tenant that consents to it, so one confirmed bad blueprint ID can be searched for across many tenants.
Detection
In Entra audit logs, look for these event pairs:
- "Create an agent identity blueprint" followed by "Add application"
- "Create an agent identity" followed by "Add service principal"
- Consent events granting permissions to an application from an external tenant, especially with
.defaultscope.
Then:
- Review agent sign-in logs for agent identities whose sponsor is an ordinary user and whose blueprint was created outside your tenant.
- Baseline which blueprints should exist, and alert on anything new.
- Because inherited permissions are hidden from the portal, inspect issued tokens (the
rolesandscpclaims) when investigating a suspicious agent.
Recommended Actions
- Restrict user consent for agent blueprints and agent identities the same way you restrict app consent. Require the admin consent workflow for third-party agents.
- Check whether MC1506733 has reached your tenant and decide whether ordinary users should be able to create blueprints at all.
- Use permission classifications so users can only approve low-impact permissions.
- Apply Conditional Access for agents and Entra ID Protection for agents where licensed.
- Review existing enterprise applications and service principals for unexpected multi-tenant agent blueprints, and remove any you do not recognise.
- Add agent-consent prompts to phishing awareness training: "connect this AI assistant" is the new "sign in to view the document".
Analyst Assessment
BluePhishing is research, not an active campaign. But consent phishing has been a reliable way into Microsoft 365 for years, and this variant gives attackers a multiplier: many identities, an irrevocable creation right, and permissions that do not show in the console. As agent platforms reach general availability and users get used to approving AI integrations, expect criminal phishing kits to adopt this quickly. Locking down agent consent now, before the rollout becomes routine, is cheap insurance.
