The Vendor You Stopped Using Still Had a Key: Qubole's Trusted AWS Role Turned Into a Front Door
2026-11-11 · By H.A

The Vendor You Stopped Using Still Had a Key: Qubole's Trusted AWS Role Turned Into a Front Door

The Vendor You Stopped Using Still Had a Key: Qubole's Trusted AWS Role Turned Into a Front Door

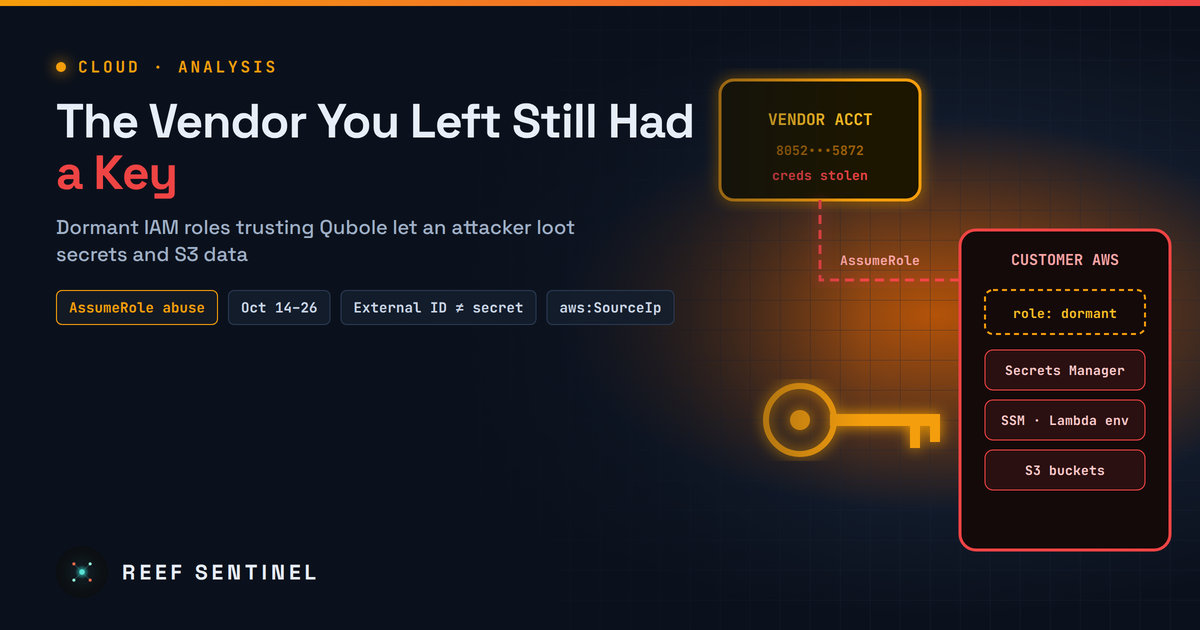
An attacker holding Qubole's own AWS credentials walked into multiple customer accounts through IAM roles that, in many cases, nobody had used in years, a reminder that cross-account trust lasts until someone deletes it.

What happened

Between October 14 and October 26, 2026, an attacker assumed IAM roles in multiple customer AWS accounts that had been set up to trust Qubole, the data lake platform now owned by Idera. Security researchers published their analysis on November 9. They say every malicious request came from Qubole's own platform account (805246085872), which also carries legitimate Qubole traffic. It is still undisclosed how the attacker got credentials for that account. When the findings came out, neither Qubole nor Idera had made a public statement, and the researchers did not give a victim count beyond "multiple" environments.

Once inside, the attacker went straight for secrets:

The researchers also found a separate burst of activity between October 8 and 11 that used customer-owned AWS access keys, which they believe had been created for Qubole integrations. They have not linked the two campaigns.

Why this is not a "Qubole bug"

Nothing here involved a software flaw. The attacker did not break IAM or AWS. They used a trust relationship exactly as it was designed to work. Many cloud services work this way: you create a role in your account, set its trust policy to allow the vendor's account to assume it, add an External ID, and attach whatever permissions the vendor's setup guide asks for. According to the researchers, Qubole's setup guide includes a sample S3 policy that grants read access to every bucket.

The worrying detail is that most of the roles the attacker assumed were dormant. They belonged to organisations that had stopped using Qubole, or barely used it, but had never removed the trust. Wiring up an integration takes an afternoon. Removing it is no one's job.

Why the External ID didn't help

The External ID is often described as a safeguard for cross-account roles. It is, but only against one specific problem, the "confused deputy", where a vendor is tricked into acting on behalf of the wrong customer. It was never meant to be a secret. AWS documents it as non-secret, it appears in plaintext in CloudTrail, and it usually sits in infrastructure-as-code files and onboarding emails. Every malicious AssumeRole request in this campaign carried a valid External ID, and every one succeeded.

Once the vendor's own account is compromised, the External ID protects nothing. The attacker is the deputy now, and an unconfused one.

The control that would have worked

The researchers say that "a source IP condition alone would have blocked every role assumption" they observed. The attacker connected from hosting and commercial VPN addresses, not from the vendor's infrastructure. An aws:SourceIp or aws:SourceVpce condition in the trust policy, limited to the vendor's published egress ranges, would have turned stolen vendor credentials into failed API calls.

That is the most useful lesson here. Most organisations audit what a vendor role can do. Few restrict where it can be used from.

The bigger pattern

This fits a pattern seen through 2026, where attackers skip the customer and go after whoever already holds the customer's trust: integration tokens, OAuth apps, managed service providers, CI/CD pipelines. Third-party access is attractive because it is pre-approved, rarely monitored and often over-privileged. A role that legitimately assumes into your account every hour looks like noise in your logs. A role that has sat unused for months and suddenly enumerates Secrets Manager should be the loudest alert you have, but only if anyone is watching for it.

Practical takeaways

aws iam list-roles --query "Roles[].[RoleName,AssumeRolePolicyDocument.Statement[].Principal.AWS]" --output json

Cross-check them against role last-used dates (aws iam get-role --role-name NAME --query Role.RoleLastUsed) and delete anything dormant.

COMPUTE NODE · · --:--:--

Fresh cybersecurity news,
daily threat intelligence.

Daily cyber news, live threat intel and exploited CVEs.

Everything in one place

Self-hosted, hardened, and yours.

RUN IT

Local AI console

Chat with a model on your own hardware via Ollama or any OpenAI-compatible server. No cloud, no key.

DEFEND

Cyber threat feed

Automatic daily intel from CISA KEV, NVD & GitHub advisories, a live cyber threat map, and your own notes.

NEWS

News & videos

Articles and updates on pentesting, AI, and cyber — with embedded video, including YouTube. Post your own.

DIRECTORY

Registry

Runtimes, models, MCP servers, agents, and a full security & pentest tooling section.

PUBLISH

Posts

Write, edit, publish, and share articles backed by a real database and your account.

COMMUNITY

Forum

Threads and replies across categories from Models to Hardware to Security.

CODE

Repos

Curated AI and security GitHub repos, plus a shelf for pinning your own.

DOWNLOAD

Skill packs

Agent starters, RAG scaffolds, and defensive security & VAPT report templates.

Registry

Runtimes, models, MCP servers, agent frameworks, and a security & pentest tooling section — all links out to the real projects.

Local AI console

Talk to a model running on your own machine through Ollama or an OpenAI-compatible server — your prompts and the model's replies always go straight from your browser to your local model, never through a Reef server. Attach files for context, and pick up saved chats where you left off.

Type /image a prompt in the box below to generate
Not connected

Local AI hardware benchmark

A spec-based compatibility advisor — tells you which local models your hardware can run well, which will be slow, and which to skip. Connect to Ollama below for a real, measured speed test instead of an estimate.

1. Your hardware

2. Live check against your local model server (optional)

If a local model server is running, this cross-references the table above with what you've actually got loaded — and runs a real, measured speed test instead of an estimate.

AI Database

A browsable catalog of AI models across providers — context windows, pricing, and capabilities.

Loading…

Cyber threat feed

Latest threats pulled automatically every day from CISA's Known-Exploited-Vulnerabilities catalog and NVD — plus threat intel you post yourself.

⇩ Export STIX
Loading threat feed…

Cyber threat map

Attacks happening right now, all over the world.

Connecting…
LIVE · MAURITIUS TIME--:--:--
attack route, country to country attack route into Mauritius attacker reported worldwide
Loading live data…
attackers reported per minute · click to rewindnow

Top attack routesweb

Attackers based inlast hour

Networkslast hour

Click any dot, feed row or table row to see that IP's profile.

Mauritius

Who attacks Mauritius

Loading…

Web attacks malicious requests to Mauritian websites that were blocked
Network DDoS floods meant to knock Mauritian servers offline

    Mauritius · last 24 h

    How Mauritius is attacked

    Network-level attacks (DDoS) aimed at Mauritius, by method. They try to knock servers and networks offline by sheer volume.

    • Loading…

    The ports or services these floods aimed at aren't published.

    Mauritius · last hour

    Attackers located in Mauritius

    0attackers located in Mauritius were reported in the last hour

    This counts attacks coming from Mauritius, not attacks on it: IPs in Mauritius that servers elsewhere reported for attacking them. Usually zero or one; when it rises, it's often a hacked local server or router.

    Worldwide today

    What attackers are knocking on

    Ports most targeted across a worldwide network of sensors .

    Worldwide today

    Most active attackers

    Ranked by how many separate sensors they hit. Click a row for its profile.

    IPCountryNetworkSensors hitReports
    What you're looking at
    Blue routes

    Share of attack traffic from one country to another. Thicker, faster streams carry more. Particles show volume, not one per attack.

    Every 15 min · published 1–2 h behind
    Amber flashes

    An attacking IP that servers around the world reported in the last minute, placed where the IP is. Its targets aren't published, so there's no line.

    Every minute · shown about 1 min behind
    Locations

    IP locations are approximate (city level at best) and show where the machine is hosted, not who controls it.

    Approximate · city level at best

    News

    Articles, guides and updates on pentesting, AI, and cybersecurity — with embedded video. Add your own, including YouTube.

    Loading…

    Posts

    Loading…

    Loading posts…

    Forum

    Questions, answers, and talk about running AI locally.

    Loading forum…

    GitHub repositories

    Curated AI and security repos, plus your own pinned shelf.

    Command board

    One-liners, configs, and advice worth keeping — shared by everyone here.

    ⚠ Commands are shared with all users. Never include credentials, tokens, or internal hostnames. Review anything before you run it.
    Loading commands…

    Skill packs

    Starter files served from the API — AI agent scaffolds plus defensive security & VAPT reporting templates. Click to download.

    Loading skills…

    Threat Library

    Threat actors, malware and tools — their attack techniques, Reef Sentinel coverage and indicators of compromise.

    Loading…

    Threat Intelligence

    Curated threat write-ups, advisories and analysis — with cover media.

    Loading…

    Tutorials

    Step-by-step guides for running local AI, using the console, and tracking threats. Admins can add their own.

    Loading…

    Downloads

    Direct links to the official homepage/download page for well-known cybersecurity, penetration-testing, and local-AI software. Always verify checksums/signatures from the vendor before running anything.

    Loading…

    Terms & Conditions

    Loading…

    Help & FAQ

    Answers to common questions about Reef Sentinel, plus a formatting guide for posts, articles, and comments.


    Formatting guide

    Commands you can type into the body of a post, comment, or reply — no HTML needed. Comments and short replies only support bold, italic, and inline code.

    Contact us

    Questions, feedback, or a security disclosure? Reach us directly, or send a message and we'll get back to you by email.

    Loading…

    Send a message

    VAPT Report Generator

    Build an engagement, add findings with a live CVSS calculator, and generate a branded, print-ready report.

    Recon Toolkit

    Passive OSINT lookups for the recon phase of an engagement, plus offline hash identification and a payload cheatsheet.

    Website Checker

    Reads a website's HTTP response headers to identify its framework and server, shows any known CVEs for the exposed versions with details, and recommends what to do.

    Control panel

    Manage everything shown on the site — news & videos, posts, homepage headlines, and subscribers. Admin only.

    Overview
    Content
    Site
    Account & Security

    Email settings

    SMTP on ports 25/465/587 is blocked outbound by some hosts (e.g. DigitalOcean droplets by default) — Resend and Brevo send over their HTTPS API instead, so they work even then. Only the selected provider is used to send; the others stay saved but idle, so you can switch back any time without losing settings.

    Get a key from resend.com/api-keys. Uses the "From address" below as the sender — it must be on a domain you've verified with Resend.

    Get an API key (not an SMTP key) from app.brevo.com/settings/keys/api. Uses the "From address" below as the sender — it must be a verified sender in your Brevo account.

    "From address" and "Site name/URL" are shared by SMTP, Resend, and Brevo — they control what recipients see, regardless of which provider is active.

    Send a test email

    Sends through whichever provider is currently active above. Save your settings first if you just changed them.
