Gorbag Uses WinRAR Flaw CVE-2025-8088 to Plant BeautyStealer at Ukrainian Courts, Front-Line City Councils and a Military Aid Transport Hub
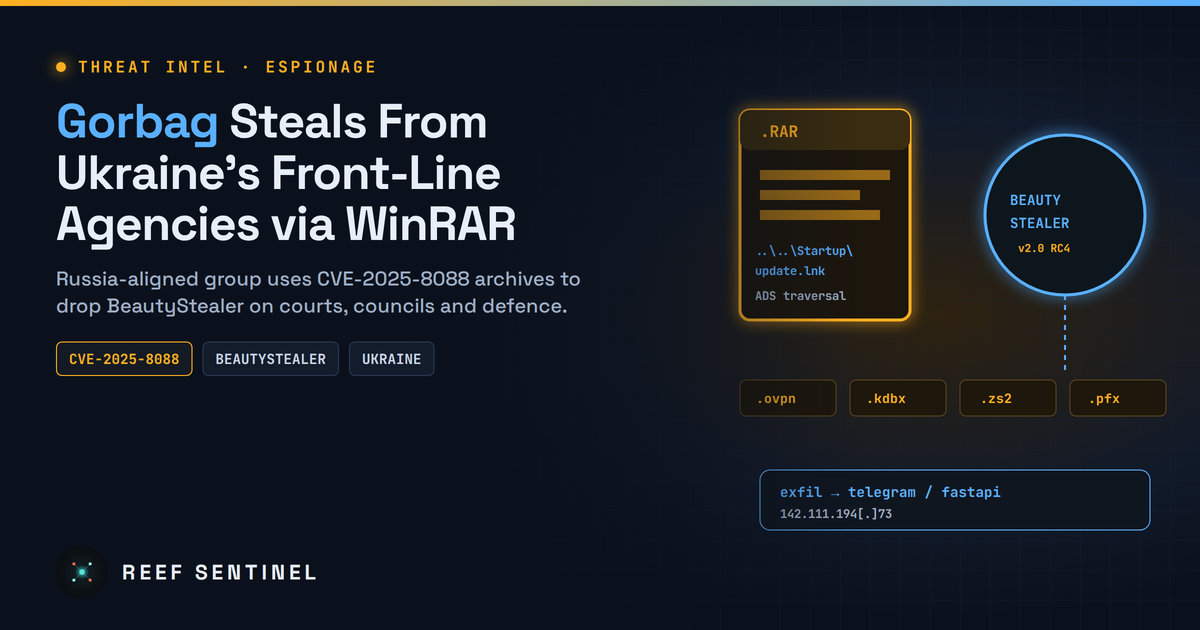
A Russia-aligned espionage group called Gorbag sends RAR archives that exploit CVE-2025-8088, some from compromised Ukrainian government mailboxes, to install BeautyStealer, which steals browser credentials, VPN profiles, KeePass databases and e-signature keys, then deletes itself.
Overview
Security researchers have documented Gorbag, a Russia-aligned espionage group that attacks only Ukrainian organizations, mostly near the front line. Since early 2026 the group has used weaponized RAR archives that exploit CVE-2025-8088, a WinRAR path-traversal flaw patched in July 2025. With them it installs BeautyStealer, a C++ infostealer that collects browser credentials, VPN profiles, password databases and Ukrainian e-signature keys in one pass, then deletes itself.
The researchers' attribution draws on overlap with UAC-0226, the cluster CERT-UA links to the GIFTEDCROOK infostealer, and on targeting that matches Russian wartime intelligence priorities. They think Gorbag may act as an initial access broker that hands stolen credentials to other Russia-aligned operators.
The Campaign
The victims fall into roughly three groups:
- About a quarter: Ukrainian justice and law-enforcement bodies
- About a quarter: local governments, mainly city councils in front-line regions
- The rest: defence-sector entities and a major transport hub that handles foreign military aid
Researchers suggest several overlapping motives: assessing battle damage after Russian airstrikes, monitoring local defence initiatives, and tracking war-crimes prosecutions.
The lures use official themes such as administrative fines and tax notices. Some were sent from compromised Ukrainian local-government mailboxes, so they look legitimate to recipients.
Timeline
- February 2025: earliest activity, when the group's first tool, Prime ReverseShell, is discovered.
- Late March 2025: first intrusions into the Ukrainian justice sector. The Prime ReverseShell C&C server is first seen on 28 March 2025.
- 2025: spearphishing uses macro-enabled Excel (.xlsm) files.
- 30 July 2025: WinRAR 7.13 fixes CVE-2025-8088, which another Russia-aligned group had already exploited.
- Early 2026: Gorbag switches to RAR archives that exploit CVE-2025-8088.
- 2 June 2026: BeautyStealer's custom exfiltration server is first seen.
- 14 October 2026: the full analysis is presented at an industry conference.
- 3 November 2026: the research is published.
Tradecraft
- Initial access (2025): an .xlsm lure runs a VBA routine that decodes a base64 payload stored in spreadsheet cells and writes it to
%ProgramData%. - Initial access (2026): a crafted RAR abuses alternate data streams to extract files outside the folder the user chose. It drops a decoy PDF, a LNK file in the Startup folder, an encrypted payload and a PowerShell loader.
- Prime ReverseShell: a PowerShell reverse shell packaged with PS2EXE and based on a public repository. It communicates over HTTPS and has not been seen since BeautyStealer arrived.
- BeautyStealer: steals cookies, saved passwords and local state from Chrome, Edge, Opera and Firefox. It also takes about 50 file types from Desktop, Documents, Downloads, removable media and mapped drives. Key targets are
.ovpn,.kdbx,.jks,.rdp,.pfxand.zs2..zs2files hold e-signature keys issued by Ukrainian accredited certification centres. - Evolution: v1.1 added file theft, v1.2 added XOR string encryption and a custom FastAPI-based server, and v2.0 added RC4-encrypted exfiltration and self-deletion through direct Windows API calls.
- Exfiltration: early versions sent data through the Telegram
sendDocumentAPI. Later versions upload to the custom server.
Indicators of Compromise
Network:
- 89.44.9[.]186 (Prime ReverseShell C&C)
- 142.111.194[.]73 (BeautyStealer exfiltration server)
Files (SHA-1):
- C17369B4B49113D07F080DF832E218156FB0940F (spearphishing email)
- A5E0A82BF6CC302A20D917235643B748F73FCC27 (Prime ReverseShell, "Windows Telemetry")
- E27E0D0A4B308F9B6B0469159931EB5E343E7FF8 (
додаток податкова.xlsmlure) - 0589D2079FBEF814DC7BB95C4B3B555C8B933AF6 (
Повідомлення 4726-49.rarexploit archive)
Vendor detection names: Win64/PSW.Agent.MA, PowerShell/ReverseShell.OB, VBA/TrojanDropper.Agent.DAT, PowerShell/Agent.EJI, LNK/Runner.FB.
Detection
- Alert on new
.lnkfiles in user Startup folders created byWinRAR.exeor shortly after a RAR file is opened. - Hunt for outbound HTTPS to
api.telegram.orgfrom workstations that have no business reason to use Telegram, especially calls tosendDocument. - Watch for one-off bulk reads of
.ovpn,.kdbx,.pfxand.zs2files followed by a compressed upload and the process deleting itself. - Search mail gateways for RAR attachments with fine- or tax-themed subjects, including ones from trusted government domains.
# Inventory WinRAR versions (anything below 7.13 is vulnerable to CVE-2025-8088)
Get-ItemProperty 'HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\*' |
  Where-Object DisplayName -like 'WinRAR*' | Select-Object DisplayName, DisplayVersion
Recommended Actions
- Update WinRAR to 7.13 or later on every endpoint, or remove it. Check bundled copies of UnRAR as well.
- Block or sandbox archive attachments from external senders, and look harder at messages from government domains, since compromised mailboxes are part of this campaign.
- If BeautyStealer may have run, revoke and reissue VPN profiles, certificates and e-signature keys, rotate passwords stored in browsers and KeePass, and invalidate session cookies.
- Block the network indicators above and check past logs for connections to them.
- Use application control to stop PowerShell and unsigned binaries from running out of user-writable folders.
Analyst Assessment
Gorbag is not technically sophisticated. It relies on an n-day WinRAR flaw, a public reverse shell and a plain stealer. Its value comes from who it targets: prosecutors, city councils and military logistics near the front line. A quick grab of credentials, VPN profiles and e-signature keys can give follow-on groups trusted access to Ukrainian state systems. The swap from Excel macros to CVE-2025-8088 shows how widely that WinRAR flaw is now used by Russia-aligned actors more than a year after the fix. Any organization that handles Ukraine-related work should treat outdated WinRAR installs as an active exposure.
