NIKKE PC Launcher Served Malware for Five Weeks: Tampered CDN Scripts Installed the K2F Remote-Access Agent and a DLL That Targets Crypto Wallets
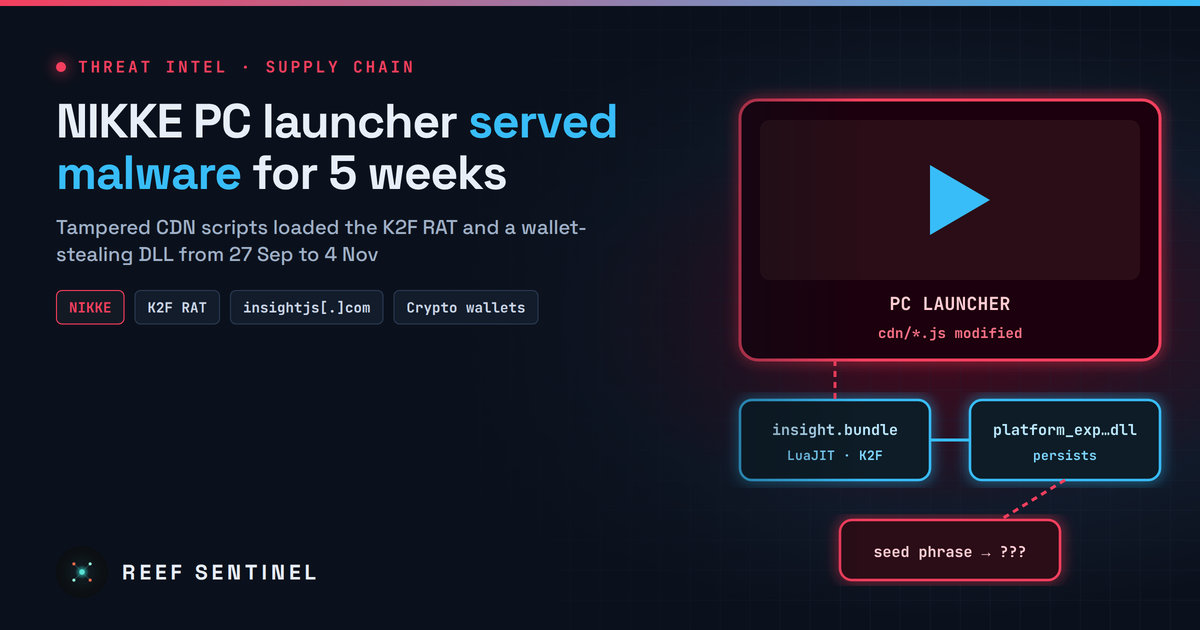
Four JavaScript files on the NIKKE publisher's official CDN were altered on 27 September 2026 to load a LuaJIT K2F remote-access agent and a persistent DLL aimed at browser data and wallet extensions, with a fixed client released on 4 November.
Overview
The PC launcher for the mobile and PC game Goddess of Victory: NIKKE (developer Shift Up, publisher Level Infinite) served malware for more than five weeks. According to an independent researcher, four JavaScript files on the publisher's official CDN were changed on 27 September 2026. When players opened the launcher, the injected code downloaded a remote-access agent from attacker servers and could also install a Windows DLL that targets browser data and cryptocurrency wallets.
The publisher acknowledged on social media that the launcher's script files "may have been tampered with by a third party" and released a fixed client on 4 November 2026 at about 02:30 (UTC+9). It says it is still investigating how many players were affected.
The Campaign
Infection chain:
- Players start the official NIKKE PC launcher, which loads JavaScript from the publisher's CDN.
- Obfuscated code hidden inside the legitimate scripts contacts
insightjs[.]com, orinsightjs[.]orgif the first domain is unavailable, and runs what it receives. - A LuaJIT payload,
insight.bundle, installs a remote-access agent called K2F. - On command, K2F installs
platform_experience_helper.dll, which keeps running after the launcher is closed.
According to the researcher, K2F can run remote commands, browse and download local files, take screenshots, steal NIKKE account credentials and collect data stored in web browsers. Strings in the DLL refer to crypto wallet browser extensions such as MetaMask, Phantom and Coinbase Wallet, including the theft of recovery phrases and private keys. It is not yet known whether the wallet component was pushed to infected machines or whether any cryptocurrency was stolen.
Timeline
- 27 September 2026: Four launcher JavaScript files on the official CDN are modified.
- 3 November 2026: According to the researcher, three of the four files are replaced with clean copies. A tampered copy of the fourth was still being served afterwards.
- 4 November 2026, ~02:30 UTC+9: A client update addressing the issue is released, and the publisher confirms possible third-party tampering.
- Ongoing: The publisher's investigation and follow-up notice are pending.
Tradecraft
- Abuse of a trusted delivery channel: Changing assets on the publisher's CDN instead of the installer binary meant that code signing and installer verification never came into play. The launcher trusted whatever its CDN served.
- Staged, modular payloads: A small loader, then a LuaJIT agent, then an optional native DLL. Expensive capabilities were only deployed where the attacker chose to use them.
- Fallback infrastructure: Primary and backup domains made the loader resilient to a single takedown. Someone, whose identity is unknown, has since put a multilingual warning page on the backup domain telling players to close the launcher.
- Target choice: Gamers often have browser wallets, saved passwords and powerful PCs, and they rarely run enterprise EDR. That makes them an attractive population for theft.
Indicators of Compromise
- Domains:
insightjs[.]com,insightjs[.]org - Files:
insight.bundle,platform_experience_helper.dll - DLL SHA-256:
4bfaf98a6b863fa79554d9eeeb18870c3f92d552d62f4bd35a72d19ea68526af - Log string
k2f_chan registeredinLauncher\intl_service\debug.loginside the NIKKE install folder. This shows the Lua agent ran but does not prove the DLL was loaded.
Detection
# Defensive: check the NIKKE launcher log for the agent marker (adjust the install path)
Select-String -Path "C:\NIKKE\Launcher\intl_service\debug.log" -Pattern "k2f_chan registered"

# Look for the persistent DLL anywhere on the system drive
Get-ChildItem C:\ -Recurse -Filter platform_experience_helper.dll -ErrorAction SilentlyContinue
Organisations should check DNS and proxy logs for the two insightjs domains, because staff may have played on work or BYOD machines.
Recommended Actions
- Update the NIKKE launcher to the 4 November build or later, and close it until you have checked the machine.
- Run a full scan with up-to-date antivirus and check the log marker and DLL above.
- If either indicator is found, back up personal files and reinstall Windows. The RAT could have installed other payloads.
- From a clean device, change passwords saved in browsers, sign out of all sessions, and reset NIKKE, email and gaming platform accounts.
- If a crypto wallet extension was installed, consider the recovery phrase compromised. Create a new wallet on a clean device and move the funds.
- Block
insightjs[.]comandinsightjs[.]orgat DNS and on web proxies.
Analyst Assessment
This is a real supply-chain compromise of a widely played game. It ran for more than five weeks on official infrastructure, and it was confirmed by the publisher's own statement and by independent analysis of the loader. Most technical details still come from one researcher's analysis, and the number of affected players is unknown. Because the attacker had a full remote-access agent on player PCs and possible access to crypto wallets, we rate the threat High for anyone who opened the PC launcher between 27 September and 4 November 2026.
