3AM Ransomware Hit a UK School Estate With What Looked Like an AI Agent Loop — Rewritten Retries Every 40–100 Seconds, Veeam Credentials Stolen, 37 Machines Encrypted
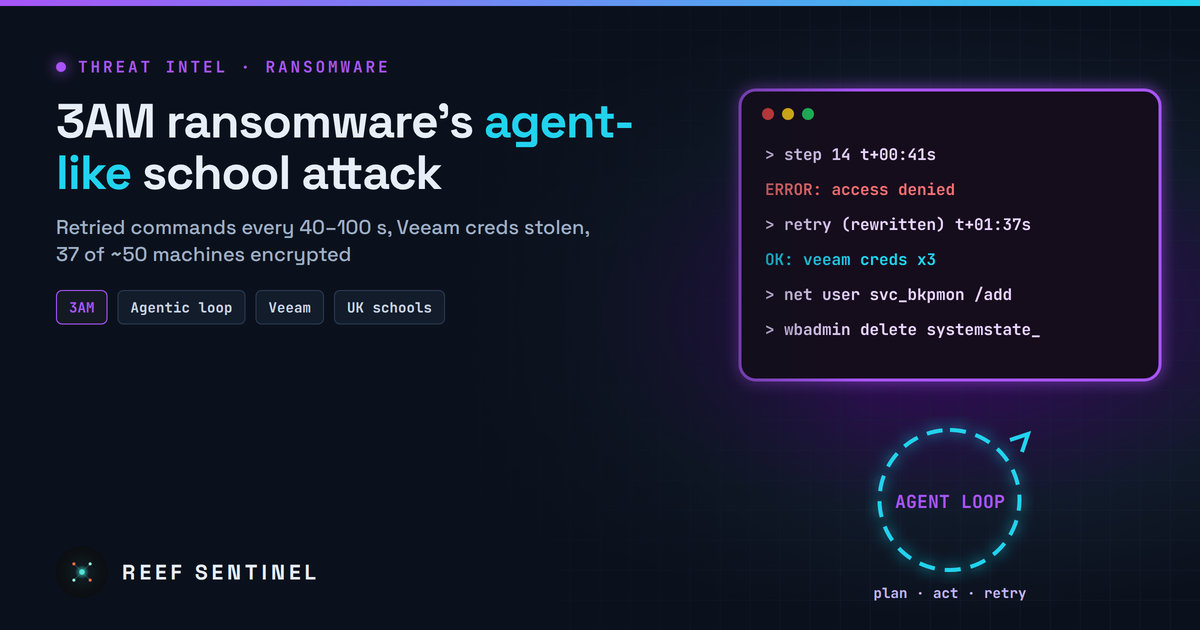
Researchers say a 3AM affiliate who encrypted about 37 of nearly 50 machines across three trusted school domains issued slightly rewritten retries at agent-like intervals, stole Veeam backup credentials and created backdoor admins 'library' and 'svc_bkpmon'.
Overview
Security researchers have published a report on a 3AM ransomware intrusion against a UK school estate between 10 and 19 September 2026. The operator reached nearly 50 machines, encrypted about 37 of them, stole financial data and destroyed backups. What makes the case unusual is how the attacker worked. The command stream looked less like a person typing and more like an agentic loop: failed commands came back slightly rewritten, and new ones arrived at fairly regular intervals of about 40 to 100 seconds.
The researchers say plainly that they cannot prove an AI model was involved. They never got access to the attacker's machine, so they cannot say which model was used, whether it ran locally or as a service, or whether a person was just copying output between an implant and a chatbot. In their view a human chose the goals and an automated agent handled the repetitive work.
The Campaign
The victim ran three Active Directory domains that had originally been separate and were later joined with two-way trusts. Those trusts gave the attacker a path from one school environment to the next. The intrusion started from an unmanaged host, a machine outside endpoint protection and central management. The initial access method has not been found.
From there the operator went straight for credential stores and recovery systems:
- A modified public PowerShell tool pulled and decrypted credentials stored on three Veeam backup servers.
- A Chrome credential database was copied.
- Mimikatz and LSASS memory-dumping tools collected more domain credentials.
- The attacker mapped domain trust relationships and searched logon-script folders for references to other schools.
- Two backdoor domain administrator accounts were created:
libraryandsvc_bkpmon. - Endpoint protection agents (Sophos and Bitdefender) were targeted for removal on reachable hosts.
- Before encryption, system-state backups were deleted and the 3AM encryptor, written in Rust, was deployed.
Timeline
- 2023: 3AM appears as a fallback payload after a LockBit deployment was blocked. Researchers later link the operation to people from the Conti and Royal ecosystems.
- 10–19 September 2026: The intrusion, privilege escalation, data theft and encryption of the UK school estate.
- 3 November 2026: The research is published on the same day the UK NCSC releases an assessment warning that AI-powered ransomware attacks on critical infrastructure are "highly likely" by 2028.
Tradecraft
Most of this is familiar ransomware tradecraft. The new part is the rhythm. Commands that failed were reissued with small syntax changes, which is how an LLM agent behaves when it reads an error and tries again. The steady 40–100 second gap between actions suggests a model call between steps rather than a human operator, who tends to work in bursts.
Some choices still look like a human was directing the work. The attacker went for backup credentials first, named a backdoor account to blend in with backup monitoring (svc_bkpmon), and looked for other schools in logon scripts. That matches the researchers' "human picks the objectives, agent executes" model. Earlier 3AM affiliates also relied on email bombing and fake IT-support calls for initial access, so defenders should not assume a purely technical entry point.
Indicators of Compromise
No network indicators or file hashes have been published. These host-level artefacts are useful for hunting:
- Newly created domain admin accounts named
libraryorsvc_bkpmon - PowerShell activity that queries Veeam configuration databases or credential stores
- LSASS access or dumps outside approved tooling
- Commands that tamper with or uninstall endpoint protection agents
- Deletion of system-state backups shortly before mass file changes
Detection
- Alert on any change to Domain Admins, Enterprise Admins and other privileged groups, especially for accounts created outside your provisioning workflow.
- Watch Veeam servers for unusual PowerShell, particularly scripts that load Veeam assemblies or read the configuration database.
- Flag retry patterns: the same command family repeated with small variations at regular intervals from a single session. This is a new but practical signal for agent-driven intrusions.
- Treat stopped or uninstalled EDR agents as a priority incident, not a health-check ticket.
# Defensive: list recently created AD accounts with privileged group membership
Get-ADUser -Filter {whenCreated -ge $((Get-Date).AddDays(-30))} -Properties whenCreated,memberOf |
  Where-Object { $_.memberOf -match 'Domain Admins|Enterprise Admins|Administrators' } |
  Select-Object SamAccountName, whenCreated
Recommended Actions
- Find and remove unmanaged hosts that can reach production domains, or isolate them.
- Review cross-domain trusts that were added for convenience after mergers or consolidations, and remove two-way trusts that are not needed.
- Keep backup infrastructure in its own credential domain. Do not let domain admins manage Veeam, and enable immutable or offline copies.
- Enable EDR tamper protection and require a separate secret to uninstall agents.
- Protect LSASS with Credential Guard or RunAsPPL, and rotate privileged credentials after any suspicious activity.
Analyst Assessment
Whether or not a model was in the loop, this intrusion matches the operating style that governments and researchers have been predicting: fast, persistent, tolerant of errors and inexpensive to scale. The defences that would have stopped it are not new. Managed endpoints, isolated backups, minimal domain trusts and tamper-proof EDR would each have broken the chain. Schools and other under-resourced sectors are the most exposed, because agent-assisted operators lower the cost of attacking many small targets. We rate the threat High.
