CVE-2026-123158: OpenSSH Password Bypass Lets Attackers Log In to Alpine Linux Servers With an Overlong Password
Critical · 2026-11-05 · By H.A

CVE-2026-123158: OpenSSH Password Bypass Lets Attackers Log In to Alpine Linux Servers With an Overlong Password

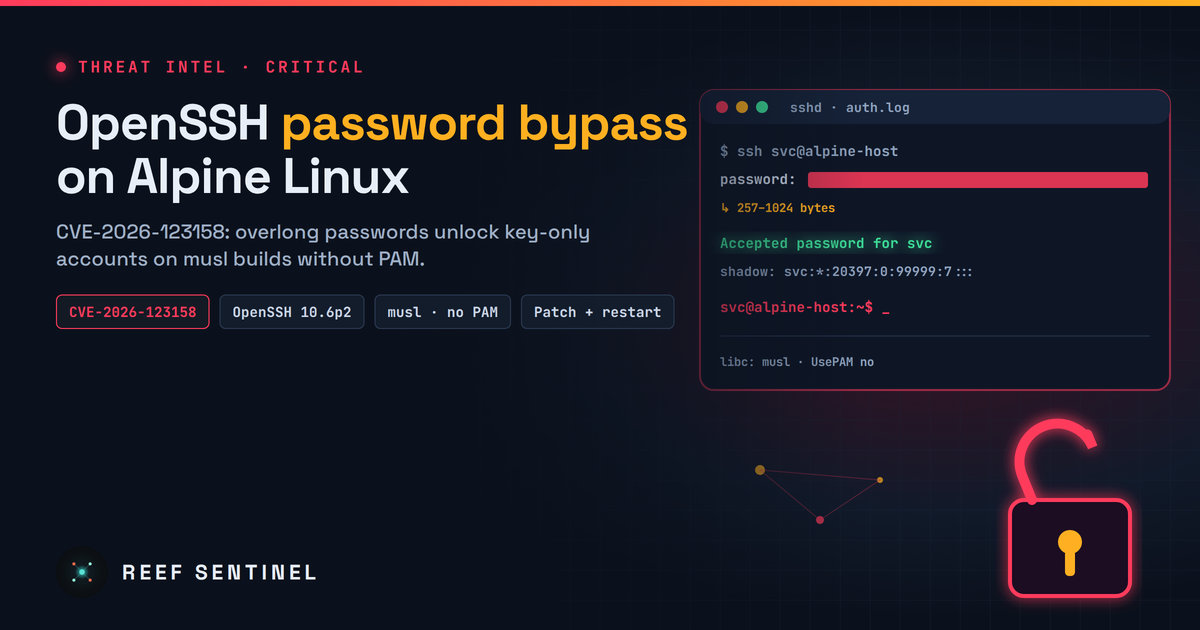
On Alpine Linux and other musl-based systems running sshd without PAM, any 257–1,024-byte password can unlock accounts marked '*', so patch to the fixed openssh package, restart sshd and disable password logins now.

Overview

A password authentication bypass in OpenSSH's server, tracked as CVE-2026-123158, lets a remote attacker log in to some Alpine Linux systems in a single attempt without knowing the password. The flaw affects Linux systems where sshd is built against the musl C library and runs without PAM. That is exactly how Alpine ships its default openssh-server package.

The OpenSSH project released portable OpenSSH 10.6p2 on 5 November 2026 with a workaround in sshd. Alpine published a security advisory the same day, along with fixed packages for every supported branch and for older branches back to 3.16. Neither the OpenSSH project nor Alpine reported exploitation in the wild at the time of publication. Because the attack is trivial once a vulnerable host is found, defenders should treat this as an emergency patch.

The Vulnerability

According to the official CVE description, sshd lacked a workaround for a password check that misinterprets whether a stored string is meant to be a password hash. On affected configurations, any password between 257 and 1,024 bytes long is accepted for certain accounts.

The OpenSSH developers say they consider the root cause to lie outside sshd itself, in how the underlying system handles the stored password value. The bug is still reachable through sshd, so it can be blocked there, and that is what 10.6p2 does.

Alpine's advisory says a host is exposed only when all of the following are true:

Accounts locked with ! are not affected. Neither are systems using PAM for password authentication, systems on glibc, or non-Linux systems. Alpine notes that root is protected by the default PermitRootLogin prohibit-password, so the realistic target is any other account marked *. Key-only accounts were never meant to accept passwords at all, so this is especially dangerous.

Affected and Fixed Versions

Supported Alpine branches 3.21 to 3.24 and edge are affected, as are the end-of-life branches 3.16 to 3.20. The fixed openssh package versions are:

New Alpine point releases 3.21.10, 3.22.8, 3.23.8 and 3.24.4 include the fix. Tiny-cloud images from 3.18.11 up to 3.24.3 are affected. Other musl-based distributions that ship OpenSSH without PAM should be checked against their own vendor's guidance.

Timeline

Tradecraft

Exploitation needs only network access to an exposed SSH port and a username of an account whose password field is *. Such accounts are easy to guess: common admin and service account names, cloud image default users, or directory accounts. The attacker then submits an overlong password in the 257 to 1,024 byte range. No brute force or credential theft is needed, and the login succeeds in one attempt.

The most likely abuse is opportunistic mass scanning of internet-facing SSH on Alpine-based virtual machines, cloud instances, appliances and containers that run sshd. Once inside, expect the usual follow-on activity: persistence through authorized_keys, new local users, privilege escalation through doas or sudo, cryptomining, and use of the host for further scanning.

Indicators of Compromise

No attacker infrastructure or malware has been published for this vulnerability. Hunt for behaviour instead (see Detection).

Detection

Check whether a host is exposed:

# package and version
apk info -v 2>/dev/null | grep -E '^openssh-server'

# effective sshd settings
sshd -T | grep -Ei '^(usepam|passwordauthentication) '

# accounts whose password field is exactly "*"
awk -F: '$2=="*" {print $1}' /etc/shadow

# accounts with $5$ / $6$ hashes
awk -F: '$2 ~ /^\$[56]\$/ {print $1}' /etc/shadow

Look for logins that should not exist:

grep 'Accepted password for' /var/log/messages

A password login for any account that has no usable password, or for an account that normally signs in only with keys, is a strong sign of exploitation. Also review recent doas use, newly created users, recently changed files and any edits to authorized_keys. Centralised logging teams should alert on Accepted password events for key-only accounts on Alpine hosts.

Recommended Actions

  1. Patch now: run apk upgrade -U -a, then restart sshd (rc-service sshd restart). Upgrading the package does not restart the running daemon.
  2. If you cannot patch immediately, turn off password logins. Create a drop-in file and restart sshd. Keep your current session open and confirm key login works first:
echo 'PasswordAuthentication no' > /etc/ssh/sshd_config.d/00-no-passwords.conf
sshd -t && rc-service sshd restart
sshd -T | grep -i '^passwordauthentication'
  1. Rebuild container images that run sshd on Alpine, and redeploy from the fixed base image.
  2. Lock key-only accounts with ! rather than * where your tooling allows it, and restrict SSH exposure with firewalls or a bastion.
  3. If you find an unexplained password login, treat the host as compromised: isolate it, rotate keys and credentials, and rebuild it.

Analyst Assessment

This is a critical, easy-to-exploit bug with a narrow but common set of conditions. Alpine is the default base for many container images, appliances and small cloud instances, and its stock SSH package has PAM off and password logins on. Many hosts will meet the conditions without their owners realising it. Accounts marked * are usually thought of as "no password", which makes the bypass especially dangerous because it hits the accounts admins consider safest.

Expect scanning to start quickly now that the trigger is public. Disabling password authentication is a reliable mitigation that costs nothing on key-based fleets, and it should be done everywhere regardless of patch status.

COMPUTE NODE · · --:--:--

Fresh cybersecurity news,
daily threat intelligence.

Run local models, watch a live threat feed, and ship security work.

Everything in one place

Self-hosted, hardened, and yours.

RUN IT

Local AI console

Chat with a model on your own hardware via Ollama or any OpenAI-compatible server. No cloud, no key.

DEFEND

Cyber threat feed

Automatic daily intel from CISA KEV, NVD & GitHub advisories, a live cyber threat map, and your own notes.

NEWS

News & videos

Articles and updates on pentesting, AI, and cyber — with embedded video, including YouTube. Post your own.

DIRECTORY

Registry

Runtimes, models, MCP servers, agents, and a full security & pentest tooling section.

PUBLISH

Posts

Write, edit, publish, and share articles backed by a real database and your account.

COMMUNITY

Forum

Threads and replies across categories from Models to Hardware to Security.

CODE

Repos

Curated AI and security GitHub repos, plus a shelf for pinning your own.

DOWNLOAD

Skill packs

Agent starters, RAG scaffolds, and defensive security & VAPT report templates.

Registry

Runtimes, models, MCP servers, agent frameworks, and a security & pentest tooling section — all links out to the real projects.

Local AI console

Talk to a model running on your own machine through Ollama or an OpenAI-compatible server — your prompts and the model's replies always go straight from your browser to your local model, never through a Reef server. Attach files for context, and pick up saved chats where you left off.

Type /image a prompt in the box below to generate
Not connected

Local AI hardware benchmark

A spec-based compatibility advisor — tells you which local models your hardware can run well, which will be slow, and which to skip. Connect to Ollama below for a real, measured speed test instead of an estimate.

1. Your hardware

2. Live check against your local model server (optional)

If a local model server is running, this cross-references the table above with what you've actually got loaded — and runs a real, measured speed test instead of an estimate.

AI Database

A browsable catalog of AI models across providers — context windows, pricing, and capabilities.

Loading…

Cyber threat feed

Latest threats pulled automatically every day from CISA's Known-Exploited-Vulnerabilities catalog and NVD — plus threat intel you post yourself.

⇩ Export STIX
Loading threat feed…

Cyber threat map

Attacks happening right now, all over the world.

Connecting…
LIVE · MAURITIUS TIME--:--:--
attack route, country to country attack route into Mauritius attacker reported worldwide
Loading live data…
attackers reported per minute · click to rewindnow

Top attack routesweb

Attackers based inlast hour

Networkslast hour

Click any dot, feed row or table row to see that IP's profile.

Mauritius

Who attacks Mauritius

Loading…

Web attacks malicious requests to Mauritian websites that were blocked
Network DDoS floods meant to knock Mauritian servers offline

    Mauritius · last 24 h

    How Mauritius is attacked

    Network-level attacks (DDoS) aimed at Mauritius, by method. They try to knock servers and networks offline by sheer volume.

    • Loading…

    The ports or services these floods aimed at aren't published.

    Mauritius · last hour

    Attackers located in Mauritius

    0attackers located in Mauritius were reported in the last hour

    This counts attacks coming from Mauritius, not attacks on it: IPs in Mauritius that servers elsewhere reported for attacking them. Usually zero or one; when it rises, it's often a hacked local server or router.

    Worldwide today

    What attackers are knocking on

    Ports most targeted across a worldwide network of sensors .

    Worldwide today

    Most active attackers

    Ranked by how many separate sensors they hit. Click a row for its profile.

    IPCountryNetworkSensors hitReports
    What you're looking at
    Blue routes

    Share of attack traffic from one country to another. Thicker, faster streams carry more. Particles show volume, not one per attack.

    Every 15 min · published 1–2 h behind
    Amber flashes

    An attacking IP that servers around the world reported in the last minute, placed where the IP is. Its targets aren't published, so there's no line.

    Every minute · shown about 1 min behind
    Locations

    IP locations are approximate (city level at best) and show where the machine is hosted, not who controls it.

    Approximate · city level at best

    News

    Articles, guides and updates on pentesting, AI, and cybersecurity — with embedded video. Add your own, including YouTube.

    Loading…

    Posts

    Loading…

    Loading posts…

    Forum

    Questions, answers, and talk about running AI locally.

    Loading forum…

    GitHub repositories

    Curated AI and security repos, plus your own pinned shelf.

    Command board

    One-liners, configs, and advice worth keeping — shared by everyone here.

    ⚠ Commands are shared with all users. Never include credentials, tokens, or internal hostnames. Review anything before you run it.
    Loading commands…

    Skill packs

    Starter files served from the API — AI agent scaffolds plus defensive security & VAPT reporting templates. Click to download.

    Loading skills…

    Threat Intelligence

    Curated threat write-ups, advisories and analysis — with cover media.

    Loading…

    Tutorials

    Step-by-step guides for running local AI, using the console, and tracking threats. Admins can add their own.

    Loading…

    Downloads

    Direct links to the official homepage/download page for well-known cybersecurity, penetration-testing, and local-AI software. Always verify checksums/signatures from the vendor before running anything.

    Loading…

    Terms & Conditions

    Loading…

    Help & FAQ

    Answers to common questions about Reef Sentinel, plus a formatting guide for posts, articles, and comments.


    Formatting guide

    Commands you can type into the body of a post, comment, or reply — no HTML needed. Comments and short replies only support bold, italic, and inline code.

    Contact us

    Questions, feedback, or a security disclosure? Reach us directly, or send a message and we'll get back to you by email.

    Loading…

    Send a message

    VAPT Report Generator

    Build an engagement, add findings with a live CVSS calculator, and generate a branded, print-ready report.

    Recon Toolkit

    Passive OSINT lookups for the recon phase of an engagement, plus offline hash identification and a payload cheatsheet.

    Website Checker

    Reads a website's HTTP response headers to identify its framework and server, shows any known CVEs for the exposed versions with details, and recommends what to do.

    Control panel

    Manage everything shown on the site — news & videos, posts, homepage headlines, and subscribers. Admin only.

    Overview
    Content
    Site
    Account & Security

    Email settings

    SMTP on ports 25/465/587 is blocked outbound by some hosts (e.g. DigitalOcean droplets by default) — Resend and Brevo send over their HTTPS API instead, so they work even then. Only the selected provider is used to send; the others stay saved but idle, so you can switch back any time without losing settings.

    Get a key from resend.com/api-keys. Uses the "From address" below as the sender — it must be on a domain you've verified with Resend.

    Get an API key (not an SMTP key) from app.brevo.com/settings/keys/api. Uses the "From address" below as the sender — it must be a verified sender in your Brevo account.

    "From address" and "Site name/URL" are shared by SMTP, Resend, and Brevo — they control what recipients see, regardless of which provider is active.

    Send a test email

    Sends through whichever provider is currently active above. Save your settings first if you just changed them.