Six-Month Bank Phishing Operation Runs 248 Live Lookalike Domains Against 189 U.S. Financial Firms — and Cloaks Pages So They Look Dead to Takedown Teams
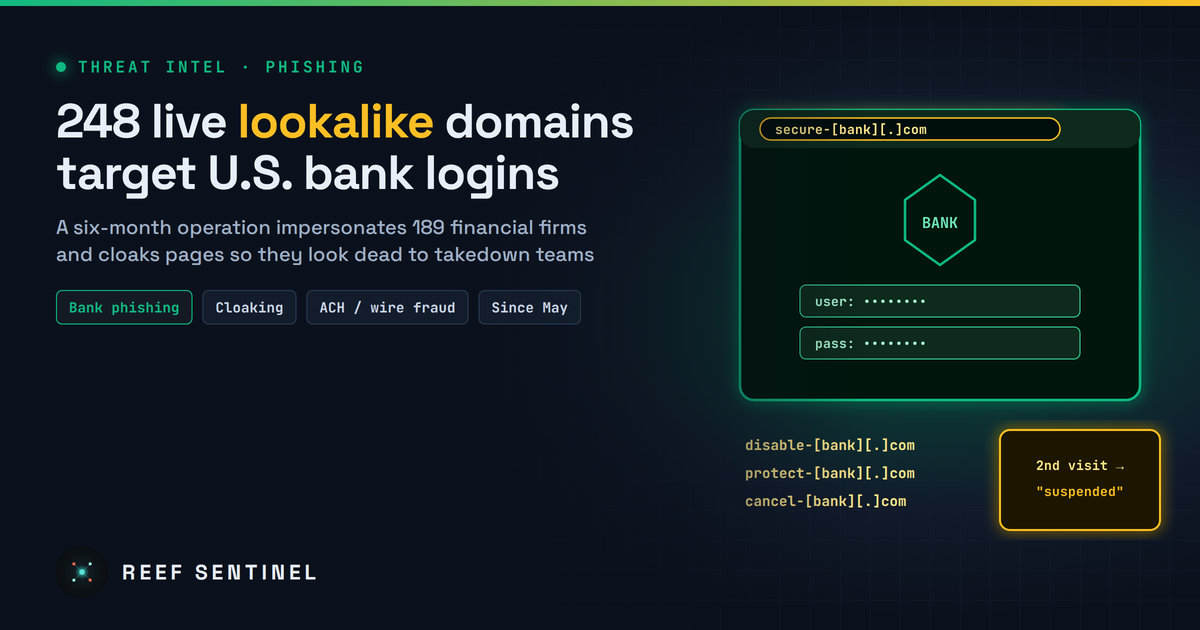
Researchers have mapped a phishing operation active since May that impersonates mostly midsize and regional U.S. banks with secure-/disable-/cancel- lookalike domains, hides behind Cloudflare and cloaking, and shares infrastructure with lures in four other countries.
Overview
Threat intelligence researchers have described a phishing operation that has been impersonating U.S. banks since May 2026 and is still active. Since May they have found more than 300 lookalike domains. On 25 October, 248 were live, impersonating 189 U.S. financial services firms, mostly midsize and regional banks. The fake login pages capture online-banking credentials that can be used for wire and ACH fraud. Researchers say the scale of use against business-banking customers is notable.
The same infrastructure also hosts lures for global crypto exchanges, users of U.S. Treasury government services, and banks, exchanges and government services in the United Kingdom, the Netherlands, Australia and New Zealand. Researchers have not determined whether this is one operator or a phishing-as-a-service platform shared by several groups. The number of victims is unknown. The researchers say they shared their findings with law enforcement and notified affected institutions before publishing.
The Campaign
- Domain pattern:
[keyword]-[bank].com, with action-style keywords such assecure,disable,protectandcancel. The names suggest lures about suspended accounts, fraud alerts or cancelled transactions. - Kit: Researchers did not find the phishing kit for sale on underground forums, which suggests private or tightly held tooling.
- Fronting: The phishing sites sit behind Cloudflare, which hides the origin servers.
- Cloaking: Repeat visits from the same IP get a fake "account suspended" notice, a different decoy page, a block, or a redirect to Google search. In the researchers' words, the goal is that "a live domain can look dead to scanners and takedown teams."
Timeline
- May 2026: First impersonation domains appear on the initial hosting provider.
- September 2026: The operation moves to a second hosting provider.
- 11 and 20 October: An apparent operator IP is seen connecting to the back end by remote desktop.
- 25 October: 248 domains live, impersonating 189 U.S. financial firms.
- 3 November: Findings published; the campaign is still active.
Tradecraft
The infrastructure has two layers:
- Front end: Disposable phishing domains on shared hosting. Both providers also host hundreds of unrelated sites and other phishing operations, which makes blocking by IP alone impractical.
- Back end: Separate management servers reached over SSH through a jump server. The jump server also connects to Telegram-run servers, which researchers think may point to bot-driven remote administration.
During 11 days in October, the same operator connection repeatedly visited a web server with no public domains, mostly between 05:00 and 07:00 UTC, through Mullvad VPN and Tor exit nodes. Researchers read this as a control panel someone checks routinely while hiding their address. On two occasions the connection appeared to come from a UK residential broadband line. Researchers caution that this is not conclusive and could be a proxy.
The non-U.S. lures use different naming and consumer brands, so they may be separate campaigns sharing infrastructure rather than one actor.
Indicators of Compromise
No specific domains or IPs were released publicly with the findings. The reusable indicator is the naming pattern, for example:
secure-[yourbank][.]comdisable-[yourbank][.]comprotect-[yourbank][.]comcancel-[yourbank][.]com
Detection
For banks and credit unions:
- Monitor certificate transparency logs and new domain registrations for your brand combined with the keywords above, and with other action words such as
verify,alertorunlock. - Expect cloaking. Check suspected domains from fresh IPs and residential or mobile vantage points, because a "dead" or Google-redirecting page on a second visit is itself a sign.
- In fraud analytics, flag new-payee wires and ACH batches that follow logins from new devices or anonymising networks, especially on business accounts.
For enterprises and customers:
- Block newly registered domains at DNS or the web proxy where policy allows.
- Train finance staff that banks will not send them a link to "cancel" or "secure" a transaction.
Recommended Actions
- Financial institutions: set up continuous lookalike-domain monitoring, pre-arrange fast takedown routes with registrars and Cloudflare's abuse process, and check whether your brand is already being impersonated.
- Move business-banking customers to phishing-resistant authentication (FIDO2/passkeys). Require out-of-band confirmation for new payees and high-value wires.
- Tell customers which domain your bank actually uses, and that they should type it or use the app rather than following links.
- Treasury and crypto platforms: apply the same domain monitoring. The infrastructure also serves lures for these brands.
- Report suspected domains to your bank, the impersonated brand, and the relevant national reporting channel (for example the FBI's IC3 in the U.S.).
Analyst Assessment
The campaign is not technically new. Credential-harvesting pages, cheap domains and CDN fronting are standard. What sets it apart is the persistence and breadth: six months, hundreds of domains, and a focus on regional banks whose brand-monitoring and takedown capacity is usually thinner than that of the largest institutions. The cloaking is designed to beat automated takedown pipelines, so the operation is likely to keep running until the back-end infrastructure is disrupted. Banks should assume they are on the list and test their detection against this exact naming pattern.
